Browse categories
Explore
Fiverr Pro
English
$
USD
Secure Smart Contract and dApp Development, Founder Infinity Block
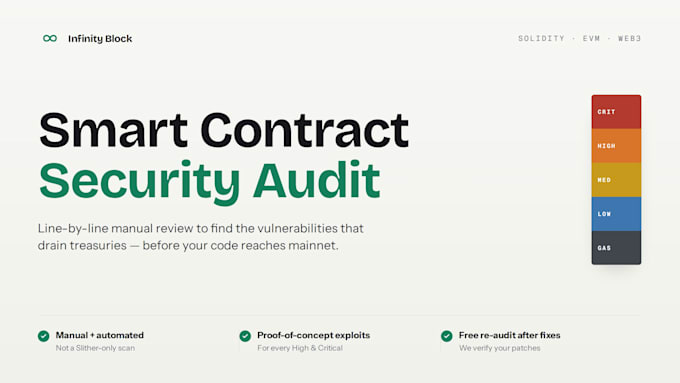
Security isn't a checkbox. I've found a live remote-code-execution backdoor hidden in a client's repo I audit like someone who's actually caught real exploits." Why me: Not assembly-line audits. Manual + automated review, real findings, clear remediation. What I check (vulnerability taxonomy): reentrancy & cross-function reentrancy, access-control flaws, integer overflow/underflow, oracle manipulation, delegatecall/proxy risks, signature replay, gas griefing, timestamp dependence, unchecked external calls, logic/economic bugs. Process: automated pass (Slither/Mythril) line-by-line manual review severity-classified report (Critical/High/Medium/Low) remediation guidance optional re-audit. Deliverable: professional PDF report with severity table, per-finding writeup, fix recommendations. Exchange/Etherscan-submittable.

Tools:
Remix
•
Ganache
•
Etherscan
Cryptocurrency services focus solely on developing and programming. Never share sensitive information or private keys with others.
How is this different from just running Slither or a free scanner?
Tools catch shallow, known patterns and miss the rest. A real audit is a human reading your code to understand how your specific protocol can be attacked especially business-logic bugs that pass every scanner. I've found live, exploitable issues that automated tools missed entirely.
Is my code kept confidential?
Yes. Your code and findings stay private and are never shared or reused. Happy to work in a private repo, and I'll delete my local copies after delivery on request.
What do you need from me to start?
Your contracts (a repo link with a specific commit, or the .sol files), a short description of what the protocol should do, and your target chain. That's enough for me to confirm scope and begin.
Which package should I choose?
Starter suits a single contract like a token or small module. Standard fits a full protocol of related contracts and is the most common. Advanced adds PoC exploits, a gas review, and a bundled re-audit. Unsure? Message me your code first and I'll point you to the right fit — no obligation.
What if you find bugs — can you fix them, or only report them?
Every finding comes with a concrete recommended fix. I can also implement the fixes for you as a separate task, then re-audit to confirm they hold.