Browse categories
English
$
USD
Connect to your AI


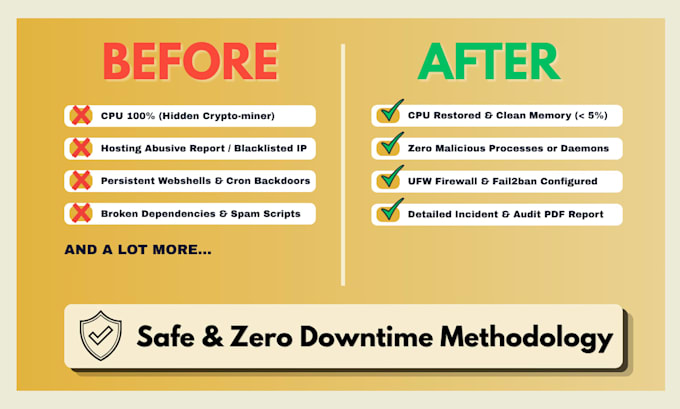
Is your Linux server hacked, running rogue crypto-miners, sending spam, or flagged by your hosting provider? I provide fast, surgical emergency cleanup and server hardening.
As a Software Architecture & DevSecOps specialist, I eliminate threats and restore your services with zero disruption to your production environment.
What I handle:
Why choose this gig?
Zero-Breakage Guarantee: Encrypted backup created prior to any remediation
Root-cause identification (patching the flaw, not just the symptom)
Professional PDF Incident Report (timeline, SHA-256 hashes, remediation advice)
Supported environments:
Ubuntu, Debian, AlmaLinux, Rocky, CentOS, Docker, Nginx, Apache.
️ Note: Feel free to send a quick message before ordering if you have specific questions or a custom setup. Let's secure your server today!
Please be aware that it is against Fiverr's policies for sellers to include themes, templates, or any other elements that infringe third-party rights or applicable laws in the delivered work. Read more about in our Guide to Responsible Digital Creation.
DevSecOps Engineer
Languages
Do I need to share my root password with you?
No, you do not need to share your root password. You can either provide a temporary sudo user or simply add my public SSH key to your authorized_keys file. Once the cleanup and audit are completed, you can easily delete the temporary account or remove the SSH key
Will my website or database be at risk during the cleanup?
Safety comes first. Prior to any remediation or file deletion, I create an encrypted local backup of your critical configuration files, web directories, and database. My interventions follow strict surgical procedures to prevent any downtime or data loss.
What information do you need to start working?
Once the order is placed, you will need to provide: your server IP address, the SSH port (default 22), the username, and either SSH credentials or permission to add my public key. A brief description of the issue (e.g., alert from hosting provider, high CPU, spam warnings) is also helpful.
How can I be sure the malware won't come back?
Removing malware without patching the entry point often leads to reinfection. With the Premium package, I do not just clean the files: I identify the root cause (vulnerable upload script, misconfigured permissions, missing firewall rules) and apply preventive hardening to block future intrusions.