Browse categories
Explore
Fiverr Pro
English
$
USD
Cybersecurity Specialist, Pentest Reports and Security Audits
I will perform a complete digital forensics investigation on your digital evidence. I use industry-standard forensic tools like Autopsy and FTK Imager to recover deleted files, analyze disk images, examine browser history, and extract digital artifacts.
My services include file recovery, disk imaging, email forensics, memory forensics, hex dump analysis, and browser history analysis. I also develop custom Python scripts and forensic tools tailored to your specific case requirements.
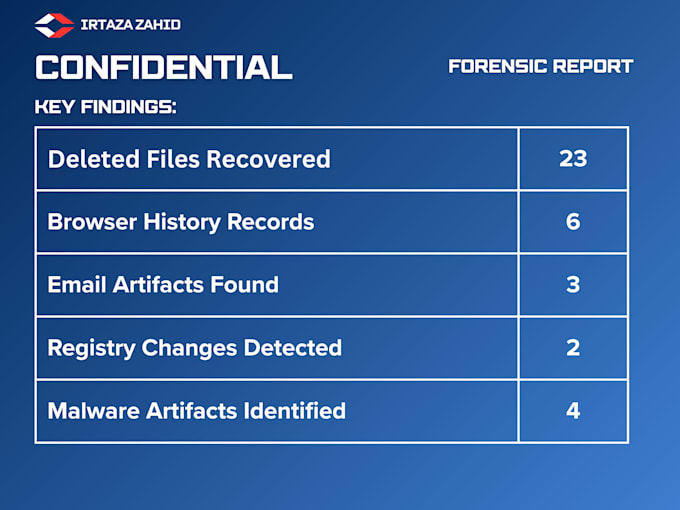
What you will receive is a professional forensic report with executive summary, detailed findings, screenshots, and evidence timeline. For premium clients, I provide court-ready reports with chain of custody documentation.
I handle all cases with complete confidentiality and am NDA friendly. All evidence is handled securely and deleted after delivery.
Whether you are a student needing a forensic report for your project, a professional investigating an incident, or a lawyer requiring digital evidence for a case, I can help.
Contact me to discuss your forensic investigation needs.


Q1. What is included in the Basic package?
The Basic package includes file recovery, deleted data analysis, and a basic forensic report with findings. It is perfect for quick data recovery and basic forensic needs
Q2. What is the difference between Standard and Premium?
Standard includes full forensic investigation using Autopsy and FTK Imager with a detailed report and screenshots. Premium includes everything in Standard plus custom Python scripts, memory forensics, email forensics, hex dump analysis, and a court-ready report with chain of custody documentation.
Q3. What types of devices and data do you work with?
I work with Windows systems, disk images, memory dumps, email files, browser history, and various forensic file formats. I can analyze hard drives, SSDs, USB drives, and memory captures.
Q4. Are my files and data safe and confidential?
Yes. All data is handled with complete confidentiality. I am NDA friendly and all files are deleted immediately after delivery. Your privacy is my priority.
Q5. Do you build custom forensic tools?
Yes. Premium includes custom Python scripts and forensic tools for your case. I have built BitLocker Key Finder, evidence parsing scripts, automated reporting, registry analysis, file carving, and log analysis scripts. Each tool is built specifically for your case with source code included.
| (1) | ||
| (0) | ||
| (0) | ||
| (0) | ||
| (0) |
melb2222

United States
Thank you!
$200-$400
Price
1 day
Duration
| (1) | ||
| (0) | ||
| (0) | ||
| (0) | ||
| (0) |
melb2222
United States
Thank you!
$200-$400
Price
1 day
Duration