Browse categories
English
$
USD
Connect to your AI
Cyber Security, Electrical Engineering Consultant
Is your website or web application really secure? Find the weaknesses before attackers do.
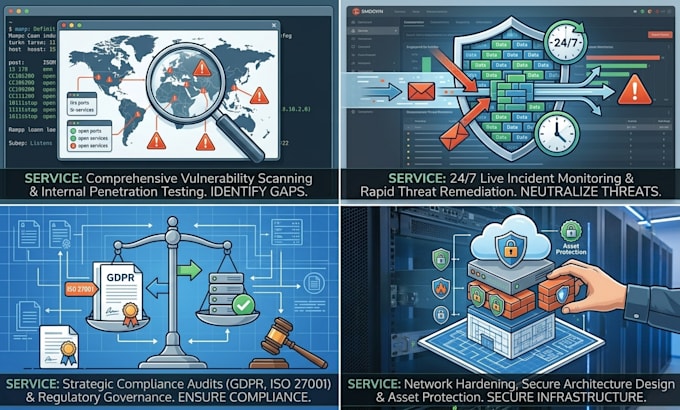
I perform web application penetration testing and vulnerability assessment, using Burp Suite, OWASP ZAP and manual testing, and deliver a clear report you can act on.
What I check
What you get
How it works
What I need from you
Target URL(s), written permission to test, and any areas to exclude.
Not included
DoS/stress testing, social engineering, and testing of systems you do not own or have permission to tes
Testing platform:
Website testing
Device:
PC
•
Linux
What do you need from me to start the security assessment?
I need the target website or web application URL, the agreed testing scope, and any necessary test credentials or access details. You must have authorization to test the target system.
What types of security testing do you provide?
I provide web application security testing, vulnerability assessment, manual security checks, and OWASP-based testing. The exact scope depends on the package you select.
Will I receive a security report?
Yes. You will receive a clear report describing identified vulnerabilities, their severity, potential impact, evidence where appropriate, and practical remediation recommendations.
Do you perform manual testing or only automated scans?
I can combine manual security testing with automated vulnerability scanning. Manual testing helps validate findings and identify issues that automated scanners may miss.
Can you test a website that is still under development?
Yes. Development and staging environments can be tested, provided that you have authorization and the environment is accessible for testing.
Can you test APIs or web application endpoints?
Yes. API and endpoint testing can be included when they are within the agreed scope. Please contact me before ordering if you require API-specific testing.
Will you fix the vulnerabilities I find?
The standard service focuses on identification, validation, reporting, and remediation guidance. Vulnerability remediation or code changes can be discussed separately depending on the project.
What if I need a larger or more complex security assessment?
No problem. If your project exceeds the scope of the listed packages, contact me before ordering. I can review your requirements and provide a custom offer.
Is authorization required for security testing?
Yes. I only perform security testing on systems for which you have explicit authorization. I do not test third-party systems without permission.