Browse categories
English
$
USD
Connect to your AI
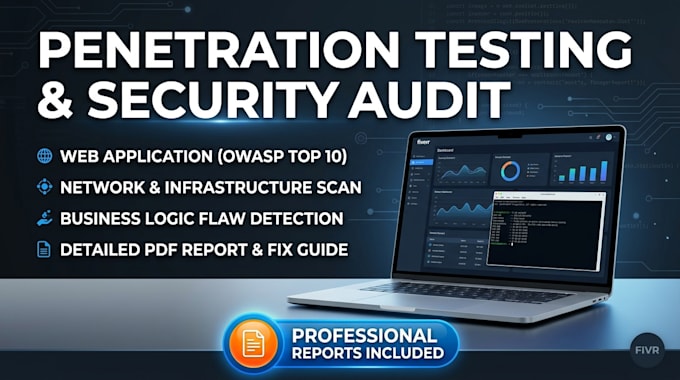
Are your website, app, or network vulnerable to cyber threats? Secure your digital assets before attackers exploit them. I provide professional penetration testing, vulnerability assessment, and quality auditing for web applications and network infrastructure.
Following industry standards (OWASP Top 10), I identify security flaws, operational bugs, and performance bottlenecks, giving your team clear steps to fix them quickly.
What I Test:
What You Get:
Ethical, confidential, and fully compliant testing. Please contact me before ordering for custom scopes or target details. (Requires authorization from target owner)
Testing application:
Website
Development technology:
Django
•
Node.js
•
Python
•
SQL
•
Swift
Device:
Mac
•
Linux
Do you require authorization before performing a penetration test?
Yes. I strictly conduct ethical penetration testing. I require confirmation that you own the target website/network or have explicit written permission from the owner before any testing begins.
Will the penetration test cause any downtime to my live website or server?
No. My testing methodology is non-destructive and safe for production environments. I perform controlled testing and can coordinate specific time windows if you prefer testing during off-peak hours.
What is the difference between an automated scan and a manual pentest?
Automated scans quickly identify known software vulnerabilities using tools. A manual pentest goes deeper—I simulate real-world hacker techniques to discover business logic flaws, complex access control bugs, and chained exploit paths that scanners miss.
Can you retest my system after my development team fixes the issues?
Yes! A free retest scan is included in the Premium package to verify that your developer patches successfully fixed the vulnerabilities. Retests can also be added as a custom gig extra.
Is my company data and testing information kept confidential?
Absolutely. All project details, target data, and report findings are strictly confidential. I am also open to signing a Non-Disclosure Agreement (NDA) prior to receiving access details.
