Browse categories
English
$
USD
Connect to your AI

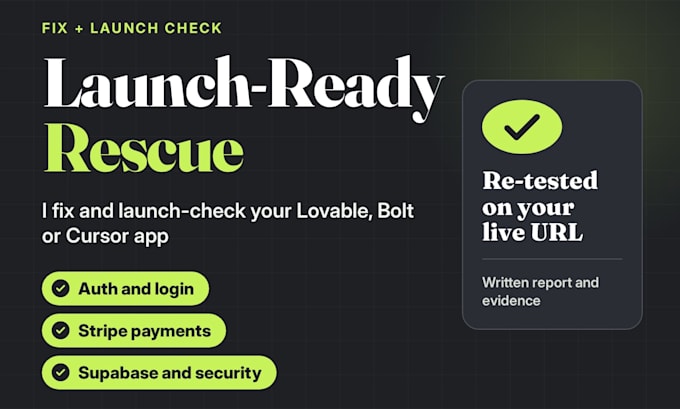
What I fix most:
How it works:
Basic: live-app scan plus the top 1-2 fixes. Standard: ONE problem fixed in your code. Premium: full 12-point launch check, report, and fixes for all Critical and High findings.
Everything is written, inside the order. No live sessions, no production secrets needed.
Not included: new features, redesigns, rewrites, app store submission, compliance certification.
AI Automation and Full Stack Developer
Languages
Which tools and stacks do you work with?
Apps built with Lovable, Bolt or Cursor. Usually React, Next.js or Vite with Supabase, Firebase or Postgres, and Stripe. If your stack is outside that, I will tell you in my first reply, before you order.
Do I need to give you my passwords or secret keys?
No. I need read access to the repo, your live URL and a test account. Never paste keys in the chat. If a key was ever shared in a chat or committed to the repo, I will tell you to rotate it.
Will you touch my live data?
Not without asking. If you have a staging copy, I use it. If not, I ask for your OK before any change that affects live data.
Can you guarantee my app is secure?
No one can. The report covers the listed checks on the date tested, with evidence. It is not a penetration test or a compliance certification.
What if you cannot reproduce my problem?
On Standard, if I cannot reproduce it within 48 hours of getting access, I cancel the order for a full refund through Fiverr. On Basic you always get the written scan result.
How do we communicate?
In writing, inside your Fiverr order: order messages, a report and code changes. This keeps the cost low and gives you a record of every change.
Can you add features or redesign the app?
Not in this gig. Order only what is broken or unsafe. I can reply with a scoped quote if you need more.
How do I describe the problem so it is fast?
Send the exact error text from the browser console or build log, what you expected, and the last change you made.
