Browse categories
Explore
Fiverr Pro
English
$
USD
Production AI, Founder led, 50 percent below agency by construction
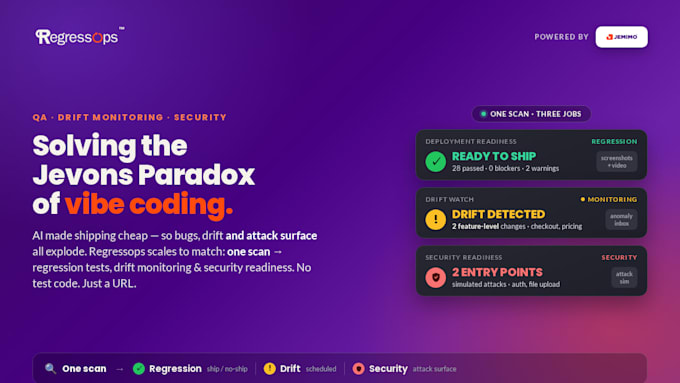
Regressops (Solving the Jevons Paradox of Vibe Coding)
AI made shipping cheap, so bugs, drift and attack surface pile up faster than any team can check them. Regressops keeps pace: one scan of your web app powers three jobs.
Regression testing it explores your app, builds a test catalog, runs it, and gives a clear ship / no-ship verdict with annotated screenshots and video evidence.
Drift monitoring scheduled or on-trigger scans catch app- or feature-level drift, surfaced in an anomaly inbox.
️ Security readiness entry-point discovery at the functionality level, simulated attacks, and a clear risk verdict before you ship.
Black-box just a URL. No test code to write. No source access needed. Works behind logins with test credentials.
Why us: an AI-native engineering practice founded by a former lead of KPMG's Gen-AI Centre of Excellence. AI-augmented delivery, humans in the loop, security baked in. 50% below agency rates by construction, not discount.
Tell us your staging URL and what "working" means for your app. We'll take it from there.


Testing application:
Web application
Development technology:
Angular
•
HTML & CSS
•
Python
•
React
•
TypeScript
Device:
PC
•
Linux
Do you need access to our code or servers ?
No — Regressops works black-box against a URL. No source access, no instrumentation. For pages behind a login, just share test credentials.
How is this different from Cypress/Selenium or hiring a QA tester?
Those need you (or a hire) to write and maintain test scripts. Regressops explores your app itself, proposes the tests, and re-runs them forever — no test-authoring, no per-hour testing cost.
Can it test flows behind a login?
Yes. Provide test credentials and it handles authenticated journeys — dashboards, checkout, account pages, and more.
Is the security testing safe? Will it break my site?
Passive checks (headers, exposed data, auth gaps) are always non-destructive. Active/simulated attacks run only on a staging URL and only with your explicit authorization — never against production without sign-off.
Do you do load or stress testing?
We report page-performance observations, but we don't do load/stress testing (simulating thousands of concurrent users) — that's a different toolset. Ask us and we'll point you the right way.
What counts as a "revision"?
A revision is a fresh re-run of the affected tests with an updated report. Included revisions cover the first re-runs; additional re-runs are available as an add-on.
Can you monitor continuously, not just once?
Yes — the Continuous Watch package wires Regressops into your CI/CD and runs scheduled drift + security checks. Ongoing monitoring is available as a monthly retainer.
What do you need to get started?
Your staging/prod URL, test credentials (if gated), a short note on your critical user journeys, and any known problem areas. We take it from there.