Browse categories
English
$
USD
Connect to your AI
IT Dev
AI tools write code that works, not always code that is safe. Typical problems: API keys left in the frontend, database tables open to anyone, missing login checks, weak input handling. I review your app for these and tell you what to fix first.
What I check (based on the OWASP Top 10):
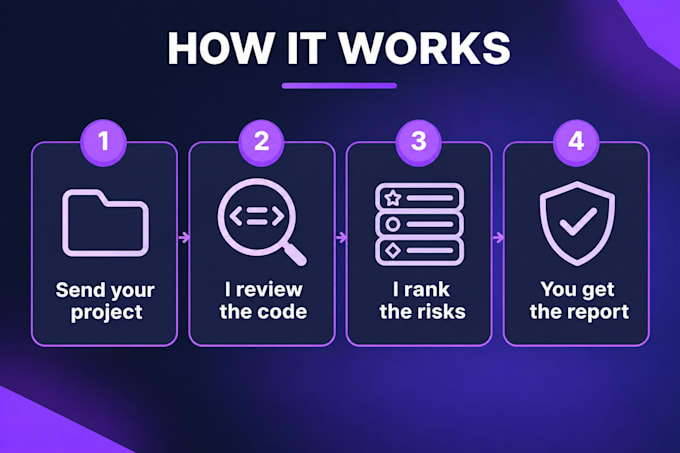
What you get: a written report ranked by risk, with a plain explanation and a suggested fix for each finding. In the higher package I apply the agreed fixes.
This is a code and configuration review, not a guarantee that the app is secure. I only review apps you own, and I never need production passwords.
I use AI-assisted tools in my workflow and review all code myself before delivery.
Development technology:
TypeScript
Expertise:
Clean Code
•
Error handling
•
Version control