Browse categories
English
$
USD
Connect to your AI
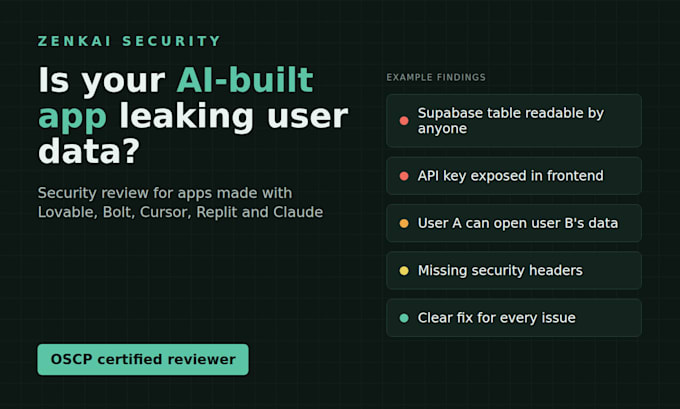

Built your app with Lovable, Bolt, Cursor, Replit or Claude? AI tools ship fast, but they repeat the same security mistakes: API keys in the frontend, open Supabase or Firebase rules, and API routes where one user can read another user's data.
I'm Joshua from Zenkai, an OSCP certified security specialist from the Netherlands. I review your app and tell you exactly what is wrong, how serious it is and how to fix it, in plain English.
WHAT I CHECK
WHAT YOU GET
HOW IT WORKS
You give me read access to your repository (or a zip). I only work on your own app, within the scope we agree on. Testing a live app is only done with your written permission.
Message me your stack before ordering and I'll confirm it fits.
OSCP Certified Ethical Hacker Pentester
Languages
Do you need access to my live app?
No. Basic and Standard only need read access to your code (GitHub invite or a zip). Live testing is only part of Premium, and only after you confirm in writing that you own the app and agree to the scope.
Which stacks do you support?
Most AI app builders and their usual stack: Next.js, React, Node, Python, Supabase, Firebase, Vercel and Netlify. Message me your stack first if you're unsure.
Will you change my code?
In Basic I only report. In Standard and Premium I fix the critical issues through a pull request you can review before merging.
Is my code safe with you?
Your code is only used for this review. I delete my copy after delivery and I'm happy to sign an NDA.
Do you use AI tools?
Yes, I use AI to speed up reading your code. Every finding is checked by me by hand before it goes in your report.
