Browse categories
English
$
USD
Connect to your AI
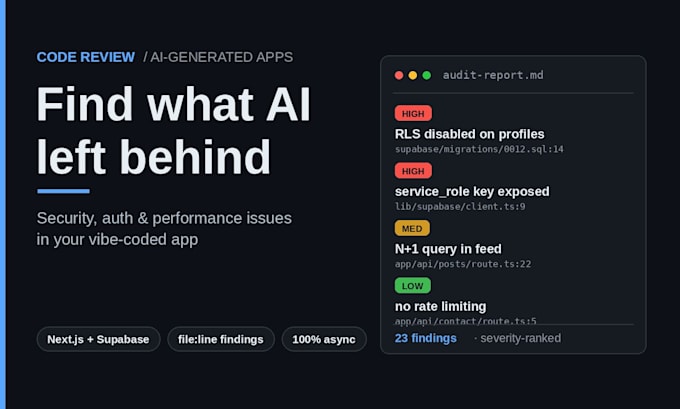
Built an app with Lovable, Bolt, Cursor, or Replit? AI writes code that runs and code that leaks. 45% of AI-generated code fails the OWASP Top 10 (Veracode).
I review your codebase and hand you a severity-ranked report: every finding with the exact file and line, what's wrong, and how to fix it. Standard and Premium also include a short screen-capture video walking through the top issues.
No calls. No production access. You give read-only repo access (or run the scanner yourself and send me the output), and you merge every fix yourself.
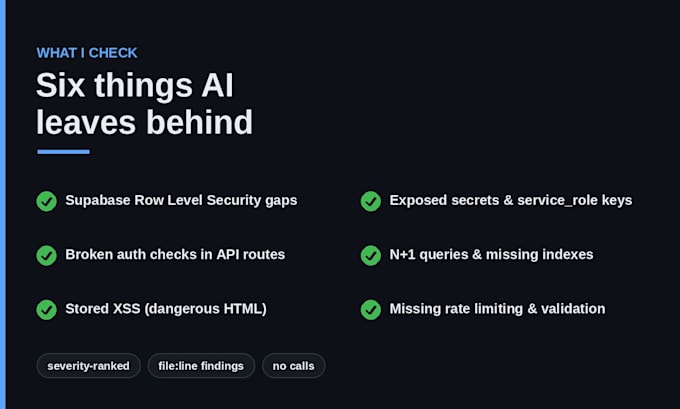
What I check (built for Next.js + Supabase):
Every finding points at a specific file and line you can verify yourself.
Development technology:
TypeScript