Browse categories
English
$
USD
Connect to your AI
Security Architect: Microsoft Sentinel, KQL, SOAR and AI Agents
Level 1
Has met certain performance criteria and shows strong potential in the marketplace.
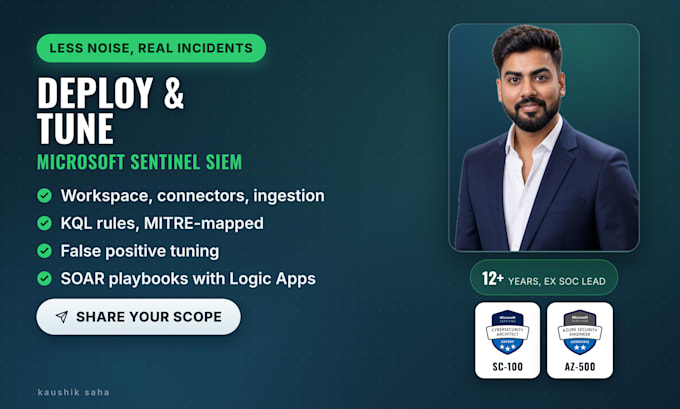
Sentinel switched on but drowning in noisy alerts? Or starting fresh and want it built right the first time?
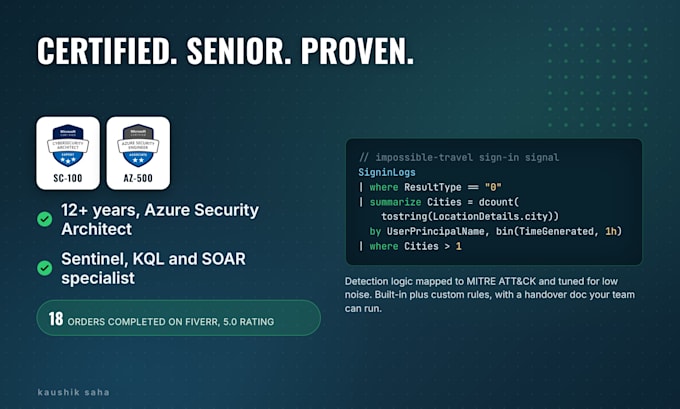
I'm Kaushik, an Azure Security Architect with 12+ years in cybersecurity. I hold SC-100 and AZ-500. I build Microsoft Sentinel the way a working SOC needs it.
What you get
Who it's for
Companies and MSSPs setting up Sentinel, or teams with a workspace that needs tuning. Works with Defender XDR and the unified Defender portal.
Message me with your scope before ordering. I'll confirm the right package or send a custom offer for larger work.
Cloud provider:
Microsoft Azure
Cloud computing resource:
Security Groups
•
Other
My Sentinel is already running but noisy. Can you tune it?
Yes. I review your analytics rules, find the ones causing false positives, tune the KQL and thresholds, and add automation rules so analysts see real incidents. Send me your noisiest rules and data sources and I'll confirm the scope.
What is included in each service package?
Basic: Sentinel deployed, 3 data sources connected, 10 built-in rules enabled. Standard: adds custom KQL rules, retention setup and a workbook. Premium: the full build with SOAR playbooks, MITRE ATT&CK mapping and cost tuning.
What information do I need to provide to get started?
Provide access to your Azure environment, details of data sources for integration, and specific objectives (e.g., threat detection, compliance, or automation). This ensures the deployment aligns with your organization's needs and goals.
Do you offer post-deployment support?
Yes. After delivery I help with managing Microsoft Sentinel, troubleshooting issues and keeping your security operations running smoothly. Extra support or team training can be arranged on request.
Can the service packages be customized to fit my organization's specific needs?
Absolutely! All packages are flexible and can be tailored to your specific needs, whether it's custom dashboards, advanced analytics, or integration with additional systems. Contact me to discuss your unique requirements.
Can you connect non-Microsoft data sources?
Yes, I support Syslog, Common Event Format (CEF), and custom connectors too.
Can you build playbooks for automated response?
Yes, I create Logic Apps that automate investigation and remediation workflows.
Will you guide me through the dashboard and rules?
Absolutely. I include documentation or a live walkthrough session (Premium only).
Is this service customizable for my environment?
Definitely. I tailor every setup to your business size, cloud usage, and threat model.