Browse categories
Explore
Fiverr Pro
English
$
USD
PNPT Penetration Tester, Web, API and Active Directory Security
Worried your web application or API has security gaps attackers could exploit? I test it the way a real attacker would and deliver a clear, actionable report.
I am a practicing VAPT Engineer and cybersecurity instructor, certified in PNPT and PJPT.
WHAT I TEST:
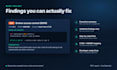
WHAT YOU RECEIVE:
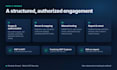
HOW IT WORKS:
See the sample report in the gallery to check the quality before you order.
Testing is non-destructive and performed only on assets you own or are authorized to test. Message me first so we can confirm scope and timeline.

Testing application:
Web application
Development technology:
JavaScript
•
Node.js
•
PHP
•
Python
•
React
Device:
PC
•
Linux
What do you need to get started?
Target URL(s), written authorization to test, an in-scope and out-of-scope list, test account credentials, and your preferred testing window.
Will testing break my website?
Testing is non-destructive by default. A staging environment is preferred, and any higher-risk test is run only with your approval.
What does the report include?
Each finding with CVSS severity, proof of concept, affected endpoints, and step-by-step remediation. Premium adds an executive summary for management.
Do you offer a retest?
Premium includes a free retest after you apply fixes. For Basic and Standard, a retest can be added as an extra.
Do you sign an NDA and keep my data confidential?
Yes. I sign NDAs on request. All findings and client data stay confidential and are deleted after delivery. I only test with written authorization.
Which tools and methodology do you use?
I follow the OWASP Web Security Testing Guide and OWASP Top 10. Tools include Burp Suite, ffuf, Nuclei, and sqlmap, but every finding is confirmed manually before it goes in the report.
Can the report help with SOC 2, ISO 27001, or client security reviews?
Yes. The report can serve as evidence of an independent penetration test for audits and vendor security questionnaires. It is a technical test, not a formal compliance audit or certification.


