Browse categories
Explore
Fiverr Pro
English
$
USD
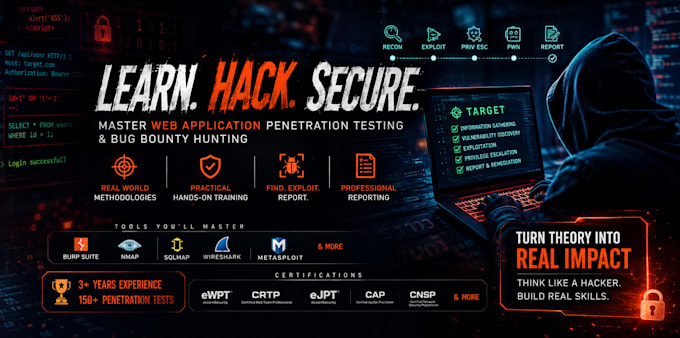
Want to learn web application penetration testing and bug bounty hunting from a cybersecurity professional?
Im a Cybersecurity Engineer with 3+ years of hands-on experience and 150+ penetration tests and vulnerability assessments across web applications, APIs, and infrastructure.
I provide practical 1-on-1 training designed to help you understand how professional security testers approach web applications and discover, validate, and report vulnerabilities.
What you can learn:
Web application security fundamentals
Reconnaissance and attack-surface discovery
Burp Suite and practical testing techniques
Authentication, authorization and IDOR
XSS, SQL Injection and other common vulnerabilities
API security testing
Business logic vulnerabilities
Vulnerability validation and proof of concept
Bug bounty methodology and workflow
Writing clear, professional vulnerability reports
Responsible disclosure and legal testing practices
My training focuses on practical methodology rather than just theory. I can adapt the lessons to your current skill level, whether you're a beginner, cybersecurity student, aspiring penetration tester, or preparing to start bug bounty hunting.


Lesson purpose:
Cybersecurity
Student age:
Teen (13–17)
•
Adult (18–65)
•
Senior (65+)
Development technology:
JavaScript
•
Python
•
PHP
•
SQL
•
Linux
•
Bash
•
Other