Browse categories
English
$
USD
Connect to your AI


Did Supabase warn you that RLS is disabled or a table is public? Can one user see another user's data? I fix your Row Level Security policies and close the gaps AI coding tools leave behind (Lovable, Bolt, Cursor, Claude Code), then re-test every fix.
AI tools write code that runs, but they often miss what only fails in production: one customer reading another customer's data, secret keys shipped inside the website, credits that break under simultaneous requests, and database writes that fail silently.
I run my own multi-tenant platform on Supabase, and I audit your app against the same 28-point checklist I use on my own system.
What I check:
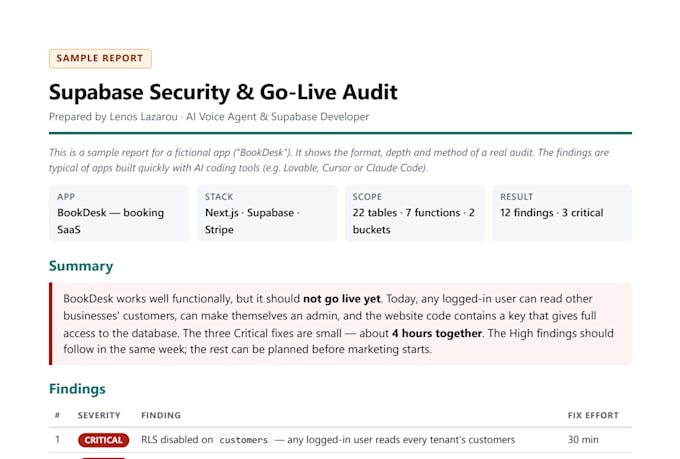
You get a written report: each finding with a severity, the evidence, why it matters and the exact fix. A sample report is in the gallery.
I work async and in writing, and I never change production without your written approval.
Supabase Audits, Booking System Fixes and AI Voice Agents
Languages
Do you need my production passwords?
No. Read access to the repository and a read-only database role (or a staging copy) is enough. Never send passwords in chat.
Will you fix the problems too?
The Premium package includes fixes for critical and high findings. For Basic and Standard, you get the exact fix for each finding.
Can we talk on a call?
I work async and in writing, so every detail is documented. Send me your questions in Fiverr messages.