Browse categories
English
$
USD
Connect to your AI
Azure and AWS Certified DevOps Engineer
Level 1
Has met certain performance criteria and shows strong potential in the marketplace.
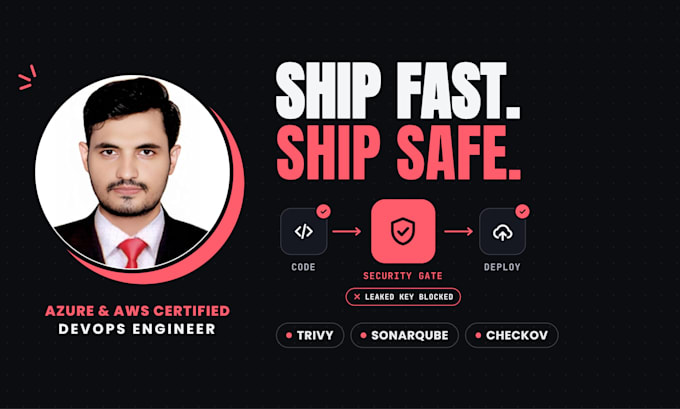
One leaked API key or vulnerable package can cost far more than a security setup. I'll add automatic security checks to your CI/CD pipeline, so problems are caught before they reach production, without slowing your team down.
What you get:
Works with GitHub Actions, GitLab CI, Azure DevOps and Jenkins.
Using AI coding tools? AI-written code can include hard-coded keys or outdated packages. These checks catch them automatically.
Why me: I'm Microsoft (AZ-104, AZ-305, AZ-400, SC-900) and AWS Solutions Architect certified, and my own pipelines are gated with Trivy and Checkov.
Every order ends with a short report: what was found, what I fixed and what to do next
Tools:
Docker
Frameworks:
Terraform
Cloud Provider:
Amazon Web Services
•
Google Cloud Platform
Programming language:
C
Expertise:
Development
Will security scans slow down my pipeline?
Usually by a minute or two. Scans run in parallel where possible, and I tune the gates so builds fail only on real risks, not noise.
Which CI tools do you support?
GitHub Actions, GitLab CI, Azure DevOps and Jenkins. GitHub Actions and Azure DevOps are my strongest.
What happens when a scan finds a problem?
The pipeline stops and shows exactly what failed and how to fix it. Add the Fix critical findings extra and I fix them for you, then rerun the checks.
Does this help with AI-generated code?
Yes. AI coding tools sometimes add hard-coded keys or outdated packages. Secret and dependency scans catch these automatically on every push.
| (1) | ||
| (0) | ||
| (0) | ||
| (0) | ||
| (0) |
rykerjakob5

United Kingdom
Abdullah did an outstanding job with my DevSecOps project! He was professional, responsive, and knowledgeable. His review of my CI/CD security pipeline and recommendations were extremely helpful. Highly recommended
$50
Price
2 days
Duration
| (1) | ||
| (0) | ||
| (0) | ||
| (0) | ||
| (0) |
rykerjakob5
United Kingdom
Abdullah did an outstanding job with my DevSecOps project! He was professional, responsive, and knowledgeable. His review of my CI/CD security pipeline and recommendations were extremely helpful. Highly recommended
$50
Price
2 days
Duration
