Browse categories
English
$
USD
Connect to your AI
Certified Cybersecurity Expert Web App Pentesting Security Audits CVSS Rep
Are you worried about your website's security? Don't just guess if you're protected. Get a real, professional audit from an expert using enterprise-grade tools.
I don't just run a basic scanner. I use RedAmon, an advanced Red Team platform, to map your entire attack surface, find real vulnerabilities, and deliver a report that looks like it came from a top-tier security firm.
**What you will get:**
* **Full Attack Surface Map:** All subdomains, open ports, and endpoints discovered.
* **Vulnerability Report:** Real findings (SQLi, XSS, BFLA) with CVSS scores and proof of concept.
* **AI-Powered Analysis:** A narrative report explaining the *impact* of each finding.
* **Actionable Fixes:** Clear recommendations to secure your site.
* **GitHub Code Fix (Optional):** If your code is on GitHub, I can even submit the exact fix via a Pull Request!
**Why choose me?**
I use professional tools (Nmap, Nuclei, RedAmon) and AI-driven analysis. You get a clean, professional PDF report you can show to your boss or clients.
**Please send me a message with your website URL before ordering so we can discuss the scope.**

Device:
Desktop
•
Laptop
•
Server
Operating system:
Windows
•
Linux
•
Unix
•
IOS
•
Ubuntu
Do you need access to my server to do the audit?
No. I do a black-box external assessment. I only need your website URL. I scan your public attack surface just like a real hacker would, without needing any credentials.
What format is the final report in?
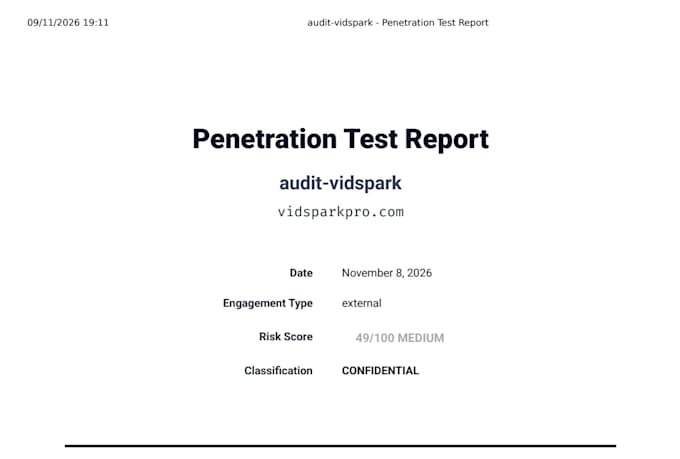
You will receive a professional PDF report. It includes the attack surface map, CVSS-scored vulnerabilities with proof of concept, and clear remediation steps. It's ready to be shared with your team or clients.
Can you fix the vulnerabilities you find?
I can provide the exact code fixes for GitHub repositories (Premium package). If your site is not on GitHub, I will provide a detailed step-by-step guide on how to fix the issues.