Browse categories
English
$
USD
Connect to your AI
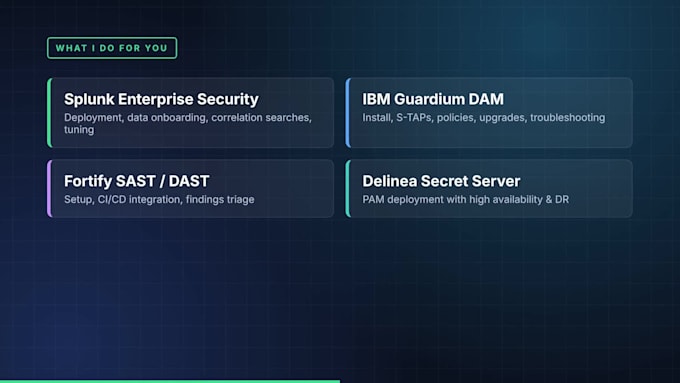
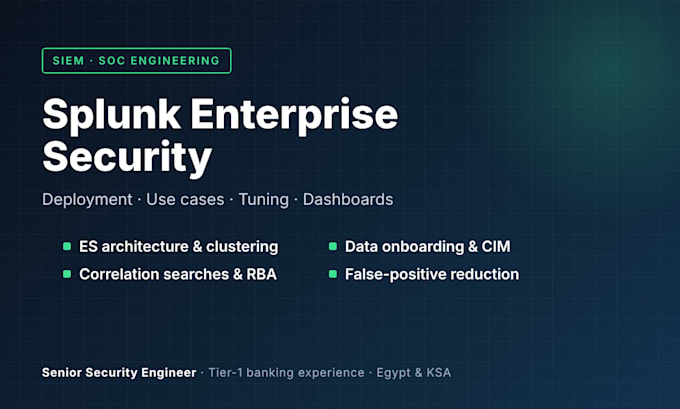
Splunk ES and IBM Guardium Security Engineer
Need Splunk to actually catch threats, not just collect logs?
I'm a Splunk Certified Admin (SPLK-1003) and Senior Information Security Engineer who has deployed and run Splunk Enterprise Security for tier-1 banks across Egypt and Saudi Arabia, including multi-site, high-availability architectures.
What I can do:
Why me: real banking-grade production experience, not lab-only knowledge. You get clean documentation with every delivery.
Please message me before ordering so I can scope your environment.
Software type:
Other
Do you work on Splunk Cloud or only on-prem?
Both. I work with Splunk Enterprise on-prem (including clustered and multi-site setups) and Splunk Cloud. Tell me your version and architecture and I will tailor the work to it.
How do you access my environment?
Your choice: a screen-share session where your team drives while I guide, or temporary access you control. I never need your passwords shared in chat, and I can work from sanitized logs and configs.
Can I order a custom package?
Yes. Most enterprise projects are different, so message me with your scope and I will send a custom offer with clear deliverables, timeline and price.