Browse categories
English
$
USD
Connect to your AI

_qqwit8.jpg)

Launching a SaaS, AI tool, or custom web application? Automated scanners miss up to 70% of critical business logic flaws and API vulnerabilities.
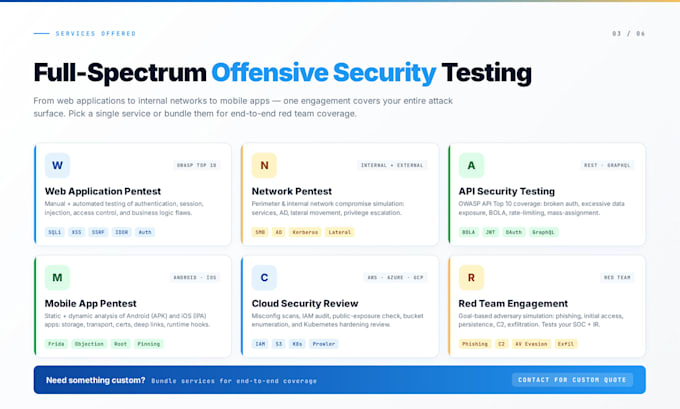
I provide manual and automated Web Application and REST/GraphQL API Penetration Testing following the industry-standard OWASP Testing Guide to ensure your platform is secure and investor-ready.
My Testing Methodology Includes:
Why Choose This Gig?
Send me a message with your tech stack and scope, and I will reply within 15 minutes!
Please be aware that it is against Fiverr's policies for sellers to include themes, templates, or any other elements that infringe third-party rights or applicable laws in the delivered work. Read more about in our Guide to Responsible Digital Creation.
Vulnerability Assessment and Ethical hacking
Languages