Browse categories
English
$
USD
Connect to your AI
DevSecOps Engineer, Server Hardening, pfSense and Secure CICD
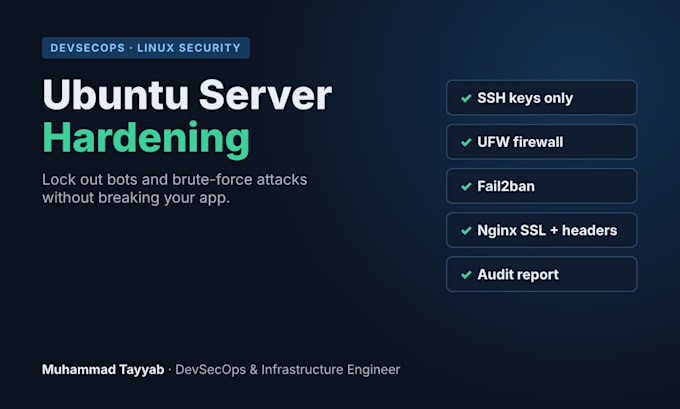
A fresh Ubuntu server is open to brute-force attacks within hours. I'll lock it down so bots, scanners and weak passwords can't get in, without breaking your app.
What I do:
Why me:
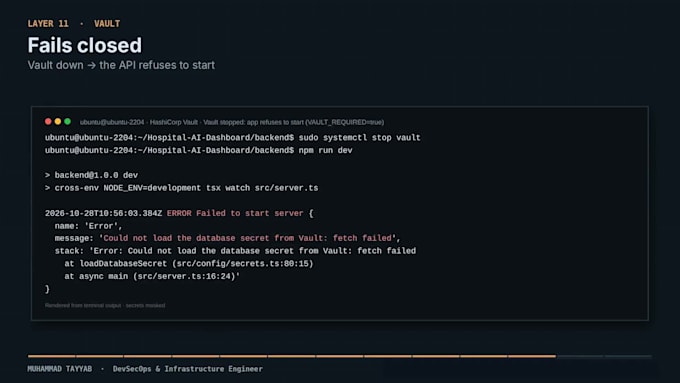
I'm a DevSecOps & Infrastructure Engineer managing production Linux servers for an EdTech company (9+ Moodle LMS instances, BigBlueButton cluster). I built a full secure infrastructure lab from the fiber line to the app: jump server, pfSense, hardened edge server and Vault.
You get: a hardened server, before/after scan, and a simple report of every change.
Message me before ordering so I can check your server and setup.
Operating system:
Linux
Will hardening break my running website or app?
No. I first check which ports and services your app uses, take a backup or snapshot, and test SSH access in a second session before closing anything. Nothing is locked until your app is confirmed working.
What do you need from me to start?
Server IP, a sudo user (or temporary SSH key access), your Ubuntu version, and a list of apps or ports that must stay open. I share a checklist after you order and remove my access when done.
Do you work on AWS, DigitalOcean or other VPS providers?
Yes. Any Ubuntu server works: AWS EC2, DigitalOcean, Hetzner, Linode, Contabo or your own VMware/on-prem server. For cloud servers I also review security groups and cloud firewall rules.