Browse categories
English
$
USD
Connect to your AI
Wazuh, Elastic SIEM and SOAR Automation Engineer
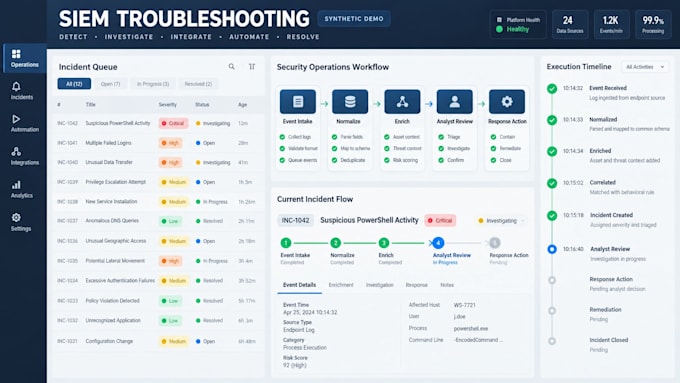
Have a SIEM issue that is blocking visibility or response? I can investigate a defined Wazuh, Elastic/Kibana, or Splunk problem, identify the likely cause, and help validate a practical fix.
Common scopes include missing or delayed events, agent connectivity, parsing/search issues, unhealthy data pipelines, dashboard or alert behavior, and a scoped SIEM-to-SOAR workflow. I can document findings and the changes made so your team has a clear handoff.
Please send the platform/version, exact error or expected-versus-actual behavior, relevant redacted logs, recent changes, and your preferred maintenance window. Each package covers a defined scope; production outages, multiple unrelated issues, log onboarding, and third-party integrations require a custom offer. Never send passwords or secrets in chat.
Server:
Virtual private server
•
Windows server
Operating system:
Windows
•
Linux
Can you fix any SIEM issue?
I first review the symptoms and logs to confirm fit. Complex or unrelated issues may need a custom scope.
Do you offer emergency 24/7 response?
Not as a standard Gig. Please confirm my availability and the scope before ordering.
Can you connect any SOAR or ticketing platform?
Only after I review the exact product, API access method, and use case. I do not promise unsupported connectors.
