Browse categories
English
$
USD
Connect to your AI
Linux sysadmin for hacked servers, OJS and Moodle
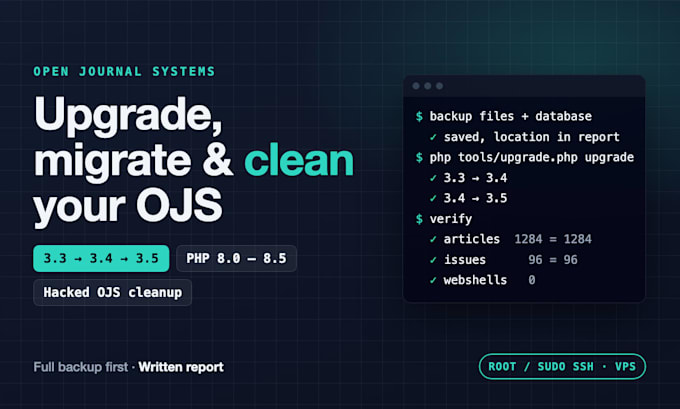
Old OJS version, broken journal, or hacked site showing gambling spam? I upgrade, migrate, repair and clean Open Journal Systems - always with a full backup first.
Upgrade & migration:
- Staged upgrades (3.2/3.3 -> 3.4 -> 3.5) without skipping required steps
- PHP 8.0 - 8.5 installed side by side, matched to what your OJS version needs
- app_key and config.inc.php fixes
- Server-to-server migration with files, database, DOIs and URLs intact
Repair:
- 500 errors, email not sending, broken theme or plugin after an update
Hacked OJS cleanup:
- Webshells and backdoors in the OJS folder and the files directory
- Gambling/SEO spam injected into articles, issues and settings in the database
- Fake admin accounts removed, entry point found and closed
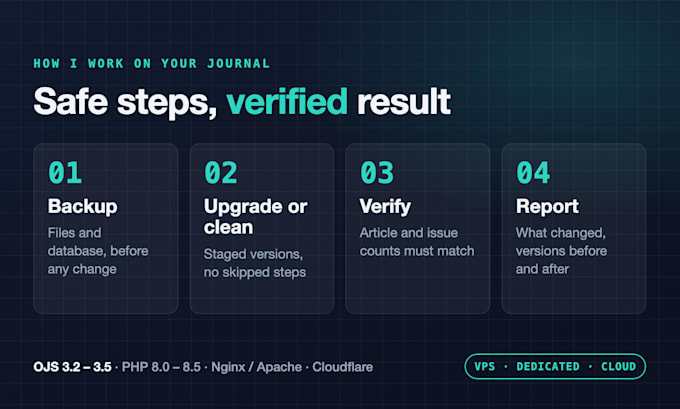
You get a written report: what was changed, versions before/after, backup location.
IMPORTANT: root or sudo SSH access is required (VPS, dedicated or cloud server). Shared hosting is not supported.
Message me first with your OJS version, PHP version and server OS.
Server:
Apache HTTP
•
Virtual private server
•
Database server
•
Nginx
Operating system:
Linux
Do you work on shared hosting or cPanel accounts?
No. I need root or sudo SSH access to a VPS, dedicated or cloud server.
Will I lose articles, issues or DOIs?
No. I take a full backup (files and database) before any change and compare article and issue counts afterwards.
Which PHP versions can you install?
Any version from PHP 8.0 to 8.5, several side by side if needed. I use the newest version your OJS supports; 8.0 and 8.1 are end-of-life, so I only use them when an older OJS still requires them.
My journal was hacked and is also outdated. What comes first?
Cleanup first, then the upgrade. Upgrading an infected install carries the backdoor along. The Premium package covers both.
Can you upgrade from OJS 2.x?
Yes, through the required intermediate versions. Please ask for a custom offer.