Browse categories
Explore
Fiverr Pro
English
$
USD
Shipped Electron App Build and Hardening Audit
Two things go wrong in most Electron apps, and neither shows in your repo.
1. The Electron security fuses stay at their defaults, so the app accepts launch arguments that hand a Node.js runtime to anything that can start it.
2. Build-time values ship in the package: source maps, dev bundles, credentials nobody meant to publish.
I audit the artifact your customers download, not your repo. Nothing runs.
You get:
- Fuse report: which hardening switches are off, and what each permits
- Build hygiene: source maps, dev bundles, auto-update channel
- Credential sweep: API keys, OAuth secrets, tokens, bundled .env files
- Endpoint and analytics inventory
- Coverage and limits: what I did not check
Not a free scanner:
- Every credential is graded; placeholders and test keys ruled out
- Secrets are masked - location and shape, never a usable key
- "Nothing found" and "nothing checkable" are different results
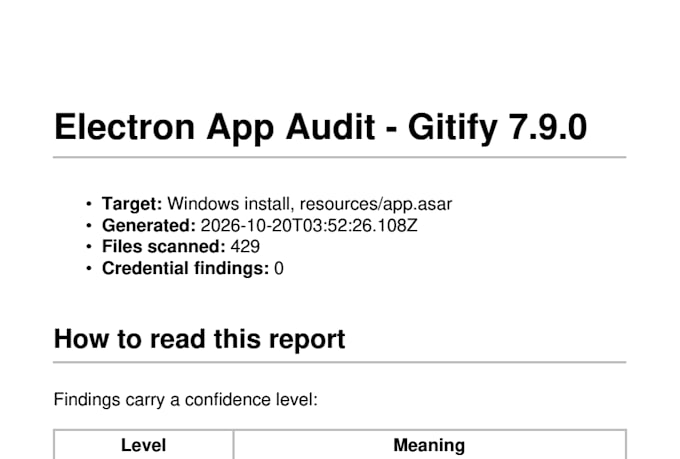
I found the fuses unconfigured in Gitify (5.4k stars); the maintainer credited the analysis in the PR adopting the fix.
Static review only. Nothing is executed.
Message me your app and platform first; I will say honestly if it is worth doing.


Development technology:
JavaScript
Expertise:
Code efficiency
•
Design patterns
•
Error handling
Do you need my source code?
No. The shipped build is the point. A source review cannot show what was baked in at package time.
Will you always find a leaked key?
No. Plenty of apps are clean on credentials and still fail on hardening. That is why the fuse and build checks are the main deliverable, not the credential sweep.
Do you run the application?
No. Static analysis of the shipped files only. Nothing is launched and no credential is tested against a live service.
Is this a penetration test?
No, and do not buy it expecting one. A penetration test attacks a running system to prove what is exploitable. This is a static review of the build: it says which hardening switches are off, what that permits, and what shipped in the package. If you need exploitation you need to find someone else.
What if you find nothing?
You still receive the report, documenting what was checked and what was out of scope. A clean result with a stated method is a useful result; a clean result with no method is worthless.
Can you fix the issues?
The Premium package includes a walkthrough call with your developer. Implementation is a separate scope and can be quoted after the report.
Is my build kept confidential?
Yes. I can sign an NDA. Findings are never published without written permission, and secret values are masked in every artifact including the report itself.