Browse categories
Explore
Fiverr Pro
English
$
USD



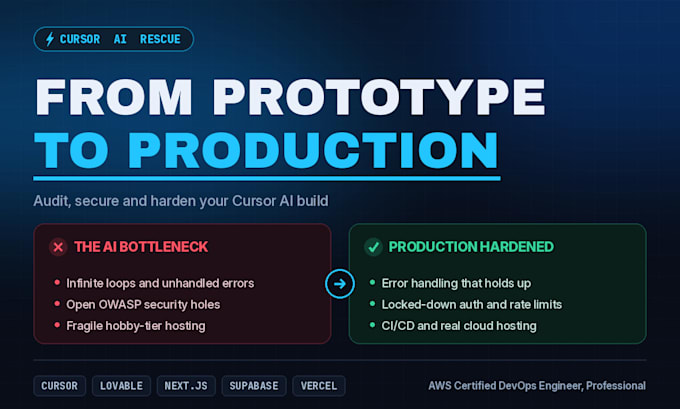
Struggling with broken code after building your MVP with AI tools?
Platforms like Cursor AI, Lovable, Bolt.new, and Replit Agent are excellent for prototyping. However, "vibe coding" introduces severe technical debt, exposed database rules, brittle LLM API integration loops, and critical security leaks that fail in production.
I am a Senior Full-Stack Engineer. I specialize in Cursor AI rescue operations, transforming fragile prototypes into secure, investor-ready SaaS applications.
What I Do:
Tech Stack: Next.js, React, TypeScript, Node.js, Express, PostgreSQL, Prisma, Drizzle ORM, OpenAI, & Claude API.
Stop wrestling with fragile prompts and exposed data. Contact me today to secure your SaaS!
Lovable app, Base44 app, Replit app, Supabase Fullstack Engineer Postgresql
Languages
What does a Cursor AI rescue engineer actually do?
A Cursor AI rescue engineer steps in when your prompt-generated application breaks. I analyze your repository, fix brittle vibe coding logic loops, resolve technical debt, and transform your fragile prototype into a stable, market-ready software application.
Why do apps built with Lovable, Bolt.new, or v0 fail in production?
While tools like Lovable, v0, and Bolt.new build beautiful frontends quickly, they lack full system context. They frequently generate hidden security leaks, weak database schemas, and unhandled API edge cases that crash under real-world concurrent user traffic.
What is included in your full technical code audit?
My comprehensive code audit thoroughly inspects your application's architecture. I look for deep logical bugs, insecure environment variables, unhandled OpenAI API cost loops, duplicate function calls, and critical back-end vulnerabilities that endanger user information.
How do you transition a fragile MVP to production hosting?
I execute a seamless cloud infrastructure migration. I move your files off hobby-tier servers to scalable architectures like Vercel, Supabase, Neon, or AWS, establishing automated GitHub Actions, CI/CD pipelines, staging setups, and secure backup routines.
Can you fix broken webhooks and LLM API cost spikes?
Yes, I specialize in stabilizing backend middleware. I implement strict rate-limiting, error fallbacks, and resilient webhook event retry queues, ensuring your OpenAI or WhatsApp API integrations do not trigger accidental billing spikes or drop essential customer data.
Do you sign non-disclosure agreements (NDAs) to protect my codebase?
Absolutely. Protecting your proprietary intellectual property and data privacy is my top priority. I am completely comfortable signing an NDA before you grant access to your repository, ensuring your startup's code remains completely secure.
Can you package my responsive web app into a mobile application?
Yes. Through custom milestones, I can seamlessly wrap your production-hardened web app codebase using hybrid frameworks like Capacitor or Cordova, preparing your platform to successfully pass review processes for the Apple App Store and Google Play Store.