Browse categories
Explore
Fiverr Pro
English
$
USD


Your AI-built app works. But can one user read another user's data?
I review Supabase/PostgreSQL apps built with Lovable, Bolt, Cursor, Replit or Base44, and I focus on what your database actually allows, not what the AI tool says it set up.
This is a manual review, not a scanner dump. Each package has a fixed amount of time, so I go deep on a defined scope instead of skimming everything.
What I check (depending on package):
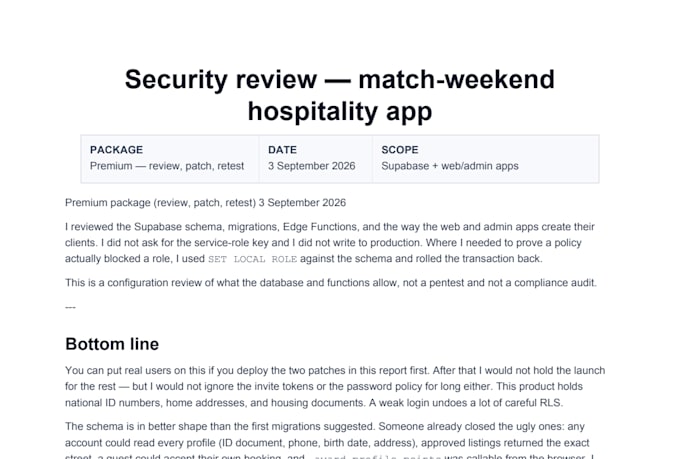
You get a report ranked by severity, with the issue, the evidence, the affected component, the risk and how to fix it.
Not included: formal penetration testing, compliance certification, or me changing your code. Need a re-check after you fix things? Add the Retest extra.
I only need read-only access or your schema/migrations. I never ask for your service-role key.
Got a long checklist? Message me first and I'll tell you which package covers it properly.
Technology Product Engineering Leader
Languages
Is this a penetration test?
No. It's a manual application and database security review. It isn't a formal pentest or a compliance audit.
Does the revision include re-checking my fixes?
No. The revision covers questions and changes to the report. Re-checking your fixes is the Retest extra, and it's included in Premium.
Can you cover Stripe, bookings, credits or other business logic?
Premium includes one business flow. You can add more flows as extras.
Can you review a single migration or a set of functions?
Yes. That's what Basic is for.
What if my app is bigger than the package limits?
I'll tell you before starting and suggest the right package or a custom offer. I won't quietly cut corners.
Do you need my service-role key or production access?
No. A read-only invite or your schema and migration files is enough. I don't make any changes to production.
Do you fix the issues?
Not as part of the packages. You get clear steps to fix each issue. If you'd like me to implement fixes, ask for a custom offer.
What if you don't find anything?
That's a good result. You still get a report showing what I checked and what I confirmed.