Browse categories
English
$
USD
Connect to your AI
Built your app with Lovable, Bolt, Cursor or Claude Code? Let's make sure it's safe before real users arrive.
AI coding tools are fast, but they often ship the same holes: exposed API keys, database tables anyone can read, no rate limits, weak logins and AI features that can leak data. I find them and fix them.
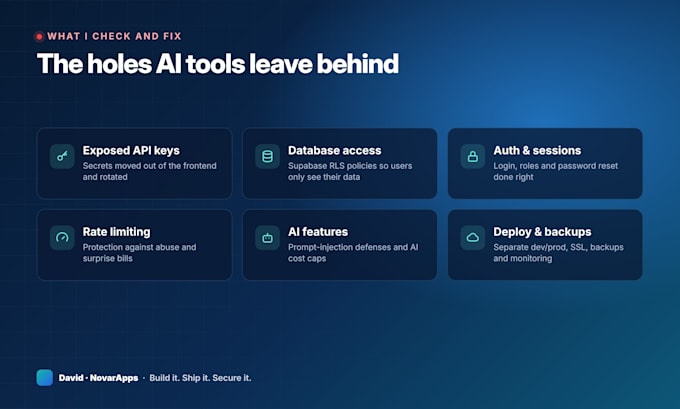
WHAT I CHECK
- Exposed API keys and secrets
- Supabase / Postgres Row Level Security (RLS)
- Authentication, roles and sessions
- Rate limiting and input validation
- AI features: prompt injection and cost controls
- Deploy: dev/prod, SSL, backups, monitoring
WHAT YOU GET
- A security report, every issue ranked by risk
- Fixes applied and verified (Standard and Premium)
- A production-ready app you understand
WHY ME
15+ years in IT, 10 running production AWS infrastructure for e-commerce, finance and logistics companies. I've shipped 7 AI-powered apps of my own and trained in offensive security (OffSec PEN-200, WEB-200, WEB-300).
Not sure which package fits? Message me with your stack and app size and I'll recommend one. The review starts once the order is placed. For larger projects, I'll send a custom offer.
Secure AI Apps, Cloud Automation, DevSecOps
Languages
Do you need access to my code?
Yes, read access to your repository (GitHub, GitLab or a zip) and, if possible, a staging URL. For Supabase, a read-only or temporary access is enough. You can revoke all access after delivery.
Will you test my live production app?
Only with your written approval and within the scope we agree on. I prefer working on a staging copy so your users are never affected.
Which tools and stacks do you work with?
Apps built with Lovable, Bolt, Cursor, Replit, v0 or Claude Code, usually React, Next.js, Node.js and Supabase or PostgreSQL, deployed on Vercel, Netlify, Render or AWS.
What if you find something you can’t fix in the package?
I’ll document it in the report with a clear explanation and send you a custom offer, with no surprises.
Is my code and data kept confidential?
Yes. I only use your code to deliver this order, I never share it, and I delete my copies after delivery if you want.
Can you also add new features or deploy my app?
Yes. Deploy is included in Premium, and for new features message me with the details.