Browse categories
English
$
USD
Connect to your AI

What you get
We fix Supabase security holes, including row level security (RLS), in apps built with Lovable, Bolt, Replit or Cursor, before real users arrive.
Basic · Database Check · $50
Read-only review of RLS, policies, grants and storage. Red/yellow/green report. The $50 is credited toward a fix ordered within 14 days.
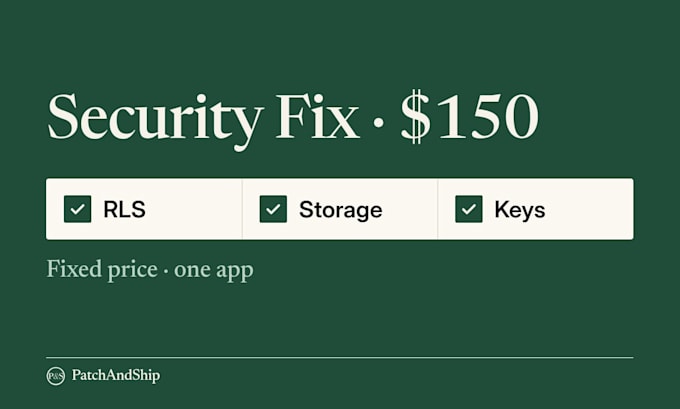
Standard · Security Fix · $150
Row Level Security on every table, storage policies, secret key scan with rotation steps, short report.
Premium · Fix and Deploy · $250
Security Fix plus live deploy on Vercel or Netlify (or Lovable/Replit hosting): env vars, auth redirects, domain with SSL, smoke test.
How we work
AI agents run the checks and a human engineer approves every change. Invites only, never passwords. You revoke us at handoff.
Guarantee
Within 48 hours of working access: critical checklist items fixed (on Premium, app live), or a full refund through Fiverr if you ask within 14 days of purchase. One app and one Supabase project per order; over 25 tables quoted first. Not a penetration test. No new features.
Message us with your stack before ordering. Never paste keys in chat.
Security fixes for Lovable, Bolt and Supabase apps
Languages
What access do you need?
Collaborator on one GitHub repo, plus a Supabase org invite (lowest role your plan allows) or, on Lovable Cloud, a Lovable Editor invite. Vercel/Netlify: guided handoff. Never passwords. Any token only via a one-time link, never in chat. You revoke us at handoff.
What does the 48 hour guarantee cover?
Critical items: RLS off or wrong, public storage with private files, exposed secret keys. On Fix and Deploy also bad env vars or auth redirects, and app live. If we miss that, a full refund through Fiverr if you ask within 14 days of purchase. Clock starts at working access.
Do you need my secret keys in chat?
No. Never paste passwords, database passwords, access tokens, service_role or sb_secret keys, Stripe live keys or .env contents into Fiverr chat or requirements. Use invites. If a key leaked, you rotate it after we remove it from code; we give exact steps.
Is this a penetration test?
No. Fixed scope for common critical issues in AI built apps on Supabase. Not a penetration test, security guarantee or compliance certification. No new features.
What if I use Bolt hosting?
Fix and Deploy deploys Bolt apps to Vercel or Netlify. We don't deploy to Bolt's own hosting. Lovable and Replit apps can stay on their own hosting with your domain.
When does the 48 hours start?
When working access is confirmed, not when you pay. Our clock pauses while we wait on you (DNS, Owner or Admin settings, key rotation). Fiverr's timer starts when you submit requirements and doesn't pause, so send the invites right after ordering.
What counts as a revision?
One round to correct anything on our checklist in this order that we missed or got wrong. A revision does not add features or new scope.
Can I see a sample report?
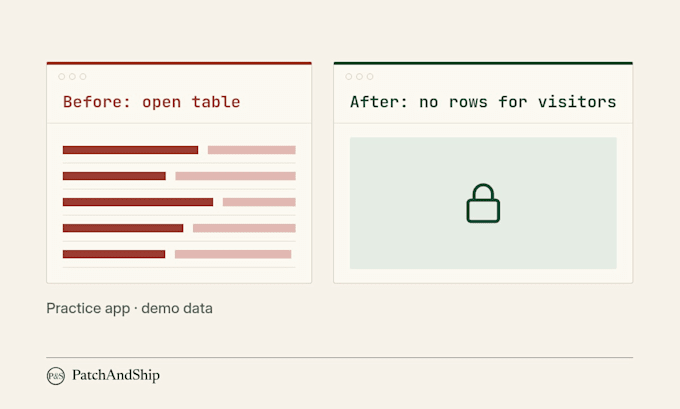
Yes. We can share an illustrative sample of our free check report format, made on fake demo data. It is not a live scan or a client result. Your paid report is different: it shows what we found and fixed, with before and after.