Browse categories
Explore
Fiverr Pro
English
$
USD
Cybersecurity and AI Automation Consultant 30 Years Network Architecture
Who I Am
30+ years in telecom and network security architecture, now helping software and hardware manufacturers meet EU Cyber Resilience Act (CRA) Article 14 vulnerability and incident reporting obligations.
What This Gig Includes
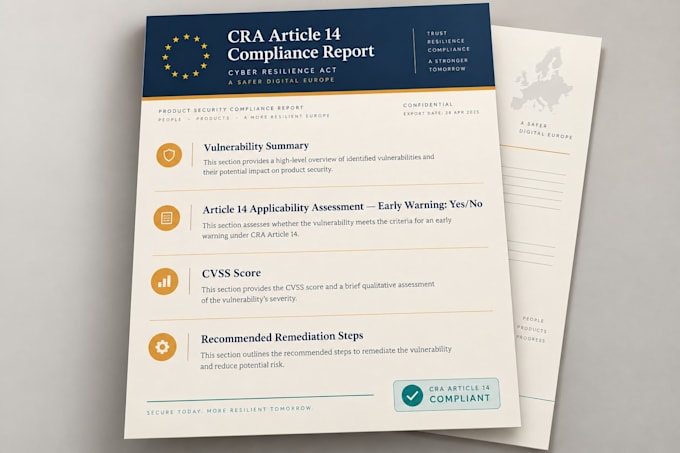
I review your reported vulnerability or security incident data against CRA Article 14 requirements and relevant severity/exploitation indicators, including CVSS, EUVD and CISA KEV where applicable. I then identify whether early-warning or incident-reporting obligations may be triggered and prepare clear documentation for your review and submission.
This gig can include:
Vulnerability/incident risk assessment
CRA Article 14 applicability review
Reporting guidance and draft documentation
Remediation recommendations
What I Need From You
Send your vulnerability report, security log, incident details or SBOM export. No credentials or live infrastructure access are required.
Let's Get Started
Choose a package and send your data through the requirements form. I will assess it and deliver the agreed report within the stated timeframe.

Business type:
Corporates
•
SMBs
Service type:
Compliance & regulatory
•
Cybersecurity risks