Browse categories
Explore
Fiverr Pro
English
$
USD

Your app works in the demo. Then someone real uses it.
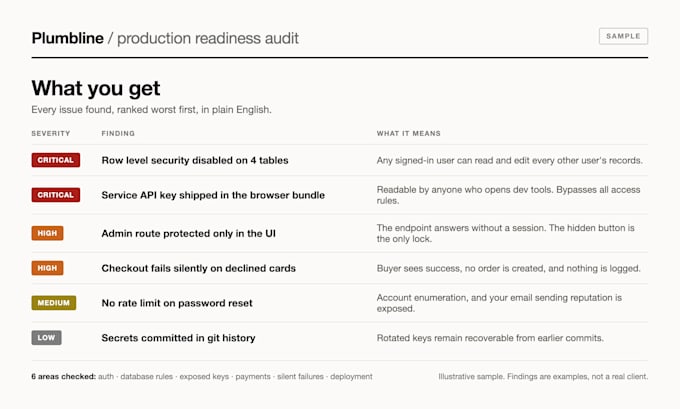
That is usually when row level security turns out to have never been switched on, an API key is sitting in the frontend bundle where anyone can read it, the login can be bypassed, or payments fail without telling anybody.
None of this means you built it wrong. AI builders optimize for a working demo, not for what keeps an app safe in public.
WHAT I DO
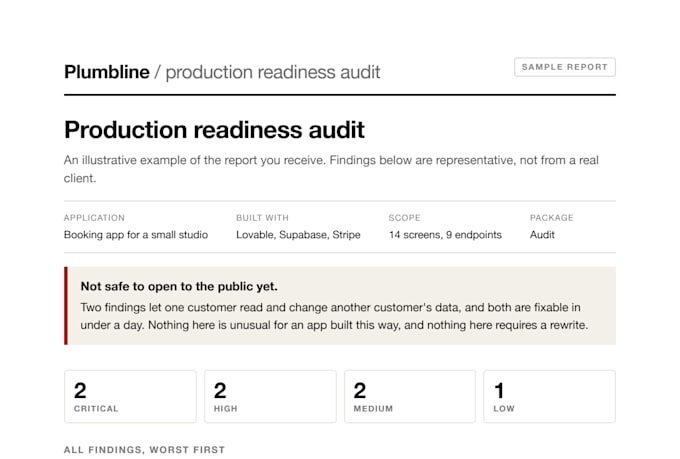
I go through your app the way an attacker and your first real customer both would. You get a report in plain English, ranked worst first: what is broken, what it costs you, and what fixing it involves. Then you decide whether I fix it or you hand it to someone else.
WHAT I CHECK
Lovable, Bolt, Replit, Base44, v0, Cursor. Usually React, Next.js, Node, Supabase.
I've spent 15+ years building production web apps. I know which problems will bite you and which are fine to leave.
You will not get a lecture about how you built it.
Send me a link and I will tell you if it is not a fit before you order.
Production hardening for AI built apps
Languages
Do you need access to my code?
Yes. A GitHub repo is best. A Lovable, Bolt or Replit project link works too. Read access is enough for the audit.
Will you fix the problems or just list them?
Basic is the report only. Standard fixes everything I rank critical. Premium fixes the medium severity issues too. You can also order the report first and add fixes afterwards.
My app is already live. Is that a problem?
No, and it is the more common case. I work against a copy where I can so nothing I do touches your live users.
I did not write this code myself. Does that matter?
Not at all. Most of the apps I see were built by someone who is not a developer, which is the point of the tools. You do not need to understand the report to act on it.
How big an app can you audit at this price?
Up to roughly 20 screens or endpoints. Send me a link before ordering and I will tell you straight if it is larger job than that.
What if you find nothing?
You get the report saying so, which is piece of mind worth having.
What languages and frameworks do you work with?
Most vibe coded apps are React, Next.js, Node and Supabase, and that is my main ground. I also work in Ruby on Rails and Python. Much of what I check, exposed keys, database rules and auth, is the same whatever the framework. Send me a link and I will tell you straight if it is not a fit.