Browse categories
English
$
USD
Connect to your AI
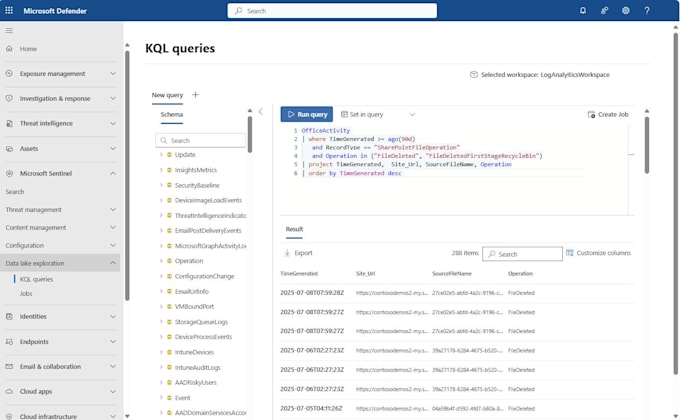
Need KQL that actually works in YOUR Microsoft Sentinel or Defender XDR?
I'm a Cybersecurity Analyst certified in Microsoft SC-200 (Security Operations Analyst) and SC-500 (Cloud and AI Security Engineer), with hands-on experience in Sentinel and Defender XDR.
Unlike generic AI-generated KQL, every query is built for your real tables and data sources, and refined based on your feedback and data.
What I can help with:
What you get:
How it works:
1. Share your goal, available tables and sanitized sample data (or the error you get)
2. I build and validate the query
3. You run it, share the results, and I fine-tune it (revisions per package)
Message me before ordering. I'll confirm the scope for free.
Do I need to provide access to my Microsoft tenant?
No. I only need your requirements and relevant table schemas or sanitized sample data.
How do you handle confidential data?
Only share sanitized data (mask usernames, IPs, domains). Everything you send is used solely for your project and deleted after delivery. NDAs are welcome.
What if the query doesn’t work in my environment?
Share the error or results and I’ll adjust it within your package revisions. Most issues are differences in table schemas or connectors and are quickly fixed.
What information should I send before ordering?
Your goal, the tables/connectors you have (e.g. SigninLogs, DeviceProcessEvents), a sanitized sample or schema, and any existing query or error message.
Do you configure Analytics Rules?
Not directly in your tenant, but I deliver the query ready to paste into an Analytics Rule, with recommended frequency, lookback period, thresholds, entity mapping and step-by-step deployment tips. Hands-on configuration can be discussed as a custom offer.
Can you troubleshoot existing KQL queries?
Yes. I can fix and optimize existing KQL, including slow queries or AI-generated ones that don’t run. Just send the original query, the error message, the expected result, and the relevant table schema or sanitized sample data.
Will you guarantee that the query detects every threat?
No tool or query can guarantee that. Detection results depend on your telemetry coverage and data quality, but every query is tailored to your environment and tuned to maximize accuracy and minimize false positives.
Do you test the queries in my environment?
Not directly. I don’t need tenant access: I validate the query against your schema and sanitized sample data, then you run it in your environment and share the results so I can fine-tune it. Testing in a non-production workspace before enabling it is always recommended.
Can you map detections to MITRE ATT&CK?
Yes. Detection rules can include the relevant MITRE ATT&CK tactics and techniques, ready to use in your Analytics Rule settings.