Browse categories
Explore
Fiverr Pro
English
$
USD
DevSecOps engineer: I deploy and secure apps for production
Built your app with AI tools or a contractor, and not sure it is safe to launch? I audit it and send you a report you can read without a security background.
What I check: secrets in the code and git history, outdated or risky packages, container and server settings, login and password reset flows, payment verification, open endpoints, HTTPS and security headers. I use scanners and check the important parts by hand.
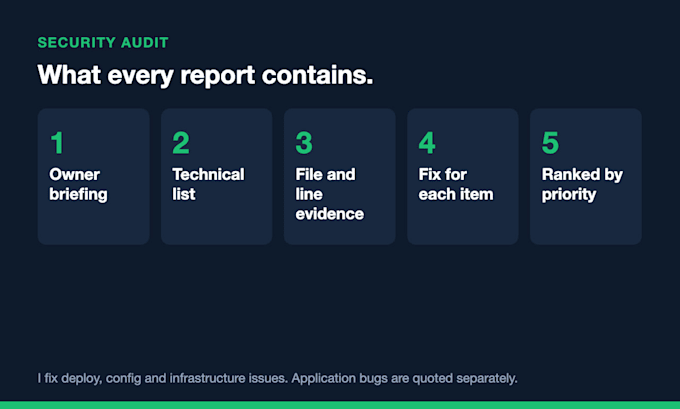
What you get: a short briefing for the owner (the three things that matter, why, how fast each can be fixed) and a technical list for your developer, with file and line evidence and a fix for each item. Findings are ranked by priority.
Recent work: for a JEE coaching institute in Bengaluru I audited four codebases, about 42,000 lines, and found 17 issues, 6 of them critical, including an unauthenticated password reset and unverified payments.
I report problems and how to fix them. I do not break into live systems, and I only test what you own and approve. Fixes are quoted separately.
Message me first with your repo link and stack.

Tools:
Docker
•
Jenkins
•
GitHub
Frameworks:
Terraform
•
Ansible
Programming language:
Java
•
JavaScript
•
Python
Expertise:
Installation
•
Debugging
•
Configuration
What do you need from me?
Read access to the repo. For a live-site test I also need your written approval and the URL. I use invited access and never ask for passwords in chat.
Do you fix the problems you find?
The report tells you exactly how to fix each item. Fixing is a separate quote. I fix deploy, config and infrastructure issues; application bugs are quoted separately.
Will you test my live site?
Only with your written yes. Without it I review the code and the setup only. I never test systems you do not own.
Is this a penetration test?
No. It is a code and configuration audit with scanner checks and manual review. It is not a certified penetration test.
Who sees the report and my code?
Only you. I do not share your code or findings with anyone, and I delete my local copy of your code after delivery.