The Dutch Cyberbeveiligingswet (Cbw), the Netherlands NIS2 law, has been in force since 15 August 2026. Is your organisation in scope, and how far are you from compliance? We give you a clear answer, fast.
Were an EU-based team headed by an experienced professional who has led security assessments at a tier-1 Dutch bank.
Our NIS2 review covers:
- Scope check: essential or important entity, sector and size
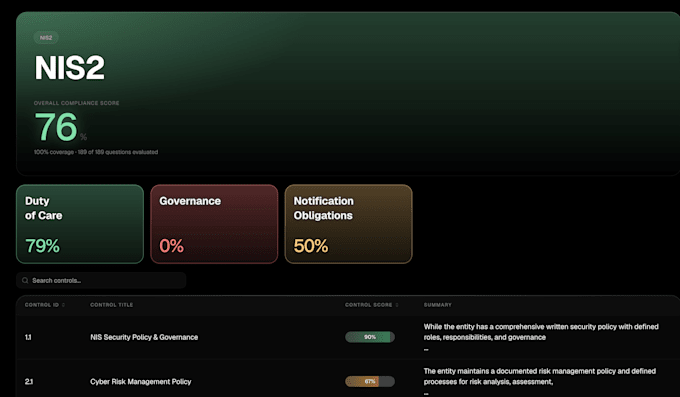
- Duty of care (zorgplicht): gap analysis of your risk-management measures against the Cbw and the Cyberbeveiligingsbesluit
- Incident reporting (meldplicht): readiness for the 24-hour, 72-hour and one-month reporting steps
- Registration duty: what you must register and with which regulator
- Supply chain: how you assess and monitor your critical vendors
- Board accountability: management oversight, approval and training duties
You receive:
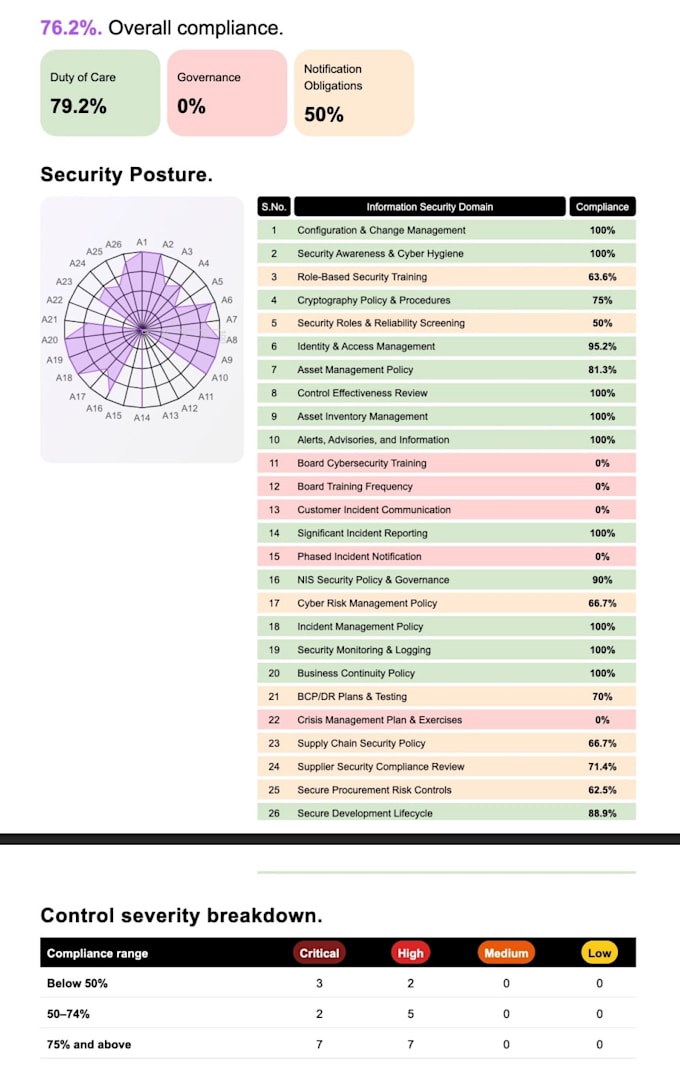
- A source-cited gap report with each gap rated by severity
- Executive summary in pdf format