Browse categories
English
$
USD
Connect to your AI
Ethical Hacker and Smart Contract Auditor for Web3 Security
Is your smart contract ready for mainnet? One missed bug can drain your liquidity in minutes.
I review your code line by line, the way an attacker would, and hand you a clear audit report with fixes.
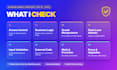
WHAT I CHECK (OWASP Smart Contract Top 10, 2026)
HOW I WORK
YOU GET
CHAINS: Ethereum, BNB Chain, Polygon, Arbitrum, Base, Avalanche (EVM) and Solana (Rust/Anchor).
Not sure which package fits? Message me your repo or contract address before ordering and I'll quote it for free.


Tools:
Slither
•
OpenZeppelin
•
Etherscan
Cryptocurrency services focus solely on developing and programming. Never share sensitive information or private keys with others.
What do you need from me to start?
Your GitHub repo (or verified contract address), the commit hash to audit, a short note on how the protocol works, and any docs or whitepaper. If you have tests, share them too.
How do you count lines of code?
I count nSLOC: real code lines, without comments, blank lines and standard OpenZeppelin imports. Send me your repo and I'll tell you the exact package before you order.
Do you audit Solana or other Rust contracts?
Yes. I review Solana programs written in Rust/Anchor as well as EVM contracts in Solidity and Vyper. Please message me first for non-EVM chains so I can confirm the scope.
Do you fix the vulnerabilities too?
The report gives a code fix for every issue. If you want me to apply the fixes in your code, add the 'Fix implementation' extra and I'll send a pull request.
Is a re-check after fixes included?
Yes. Standard includes 1 free re-check and Premium includes 2. I verify each fix and update the report status to Fixed, Acknowledged or Open.
Can you guarantee my contract is 100% safe?
No honest auditor can. An audit greatly reduces risk by finding known and logic bugs, but it is not a guarantee. I recommend tests, a bug bounty and monitoring after launch.
Will my code stay private?
Yes. Your code is used only for the audit and is never shared. I'm happy to sign an NDA, and the report is published only if you want it public.
Do you use only automated tools?
No. Tools like Slither and Aderyn catch the easy issues, but most serious bugs are logic bugs. Most of my time goes into manual line-by-line review and PoC tests.
Can I audit a token before buying or listing it?
Yes. Send the verified contract address. I check owner powers, mint, tax, blacklist, pause, proxy and liquidity risks, and explain each red flag in plain English.
What if my project is bigger than Premium?
Message me with the repo. I'll send a custom offer based on code size, complexity and your deadline.