Browse categories
Explore
Fiverr Pro
English
$
USD
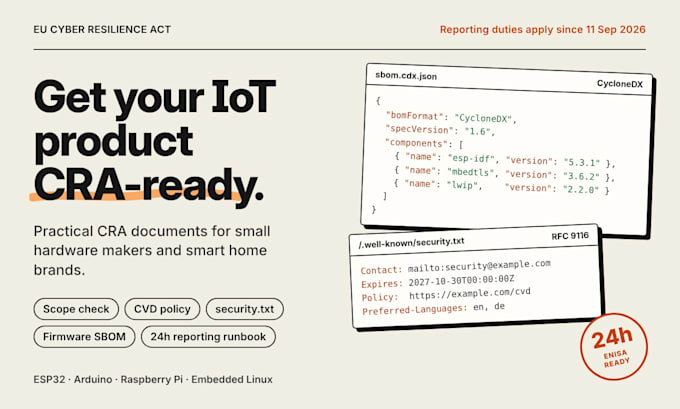
Selling a connected product in the EU? Since 11 September 2026, the Cyber Resilience Act (CRA) requires manufacturers to report actively exploited vulnerabilities within 24 hours. From December 2027, only CRA-compliant products may be sold.
I help small hardware makers, Etsy sellers, smart home brands and IoT startups get the technical CRA basics in place fast and affordable.
What you get:
CRA scope check: does your product fall under the CRA?
Coordinated vulnerability disclosure (CVD) policy + security.txt
Machine-readable SBOM (CycloneDX or SPDX) of your firmware
ENISA reporting runbook for the 24h / 72h / 14-day deadlines
Vulnerability monitoring setup for your components
Platforms: ESP32/ESP8266, Arduino, Raspberry Pi and embedded Linux.
Clear, ready-to-use documents in plain English or German.
Please message me before ordering with a short description of your product.
Note: This is technical implementation support, not legal advice and not an official certification.

Platform:
Raspberry Pi
Expertise:
IoT
•
Programming
Does the CRA apply to my product?
If your product contains software, connects to a device or network and is sold in the EU, it most likely does. The Basic package clarifies this for you in writing.
I’m a small business – do I really need this?
Yes. The CRA applies regardless of company size. Micro and small enterprises get some relief on fines for the 24-hour deadline, but they still have to report.
What do you need from me?
A product description, your firmware (repository or binary), a list of used libraries if available, and the EU countries you sell in.
Is this legal advice or a certification?
No. I deliver the technical documents and processes. For legal questions please consult a lawyer. If your product class requires it, conformity assessment is done by a notified body.
Which SBOM format do you use?
CycloneDX or SPDX, both machine-readable as the CRA requires. You choose.
