Browse categories
English
$
USD
Connect to your AI

Supabase makes it very easy to ship a database and very easy to leave it open. Row Level Security is off until you turn it on, and a policy that looks right in the dashboard can still let one customer read another customer's rows.
I run four products on Supabase in production, including a multi-tenant booking platform where salons must never see each other's customers. That is the problem I work on every week.
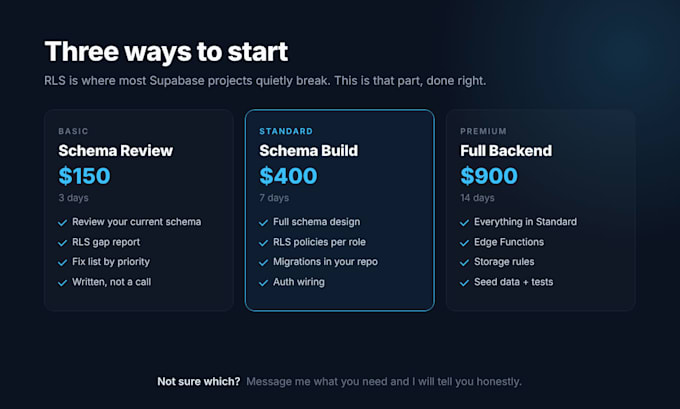
What you get: a schema designed around how your app actually queries, tables and relations with real constraints instead of loose text columns, RLS policies written per role and tested with a second account, auth wiring that matches those policies, and migrations committed to your repository so the next change is not a dashboard click nobody can trace.
If you already have a schema, start with the review package. I will send you a written report of where your data is exposed and what to fix first, and you can hand that to any developer, including me.
Send me your table list or a link to your repository and I will tell you honestly which package fits before you order.
Full stack AI engineer, Next js, Supabase, Claude API
Languages
Do you need access to my Supabase project?
For the review package no, a schema dump is enough. For build work it is easiest if you invite me to a staging project. I never ask for your production service role key.
My app is already live. Can you fix RLS without breaking it?
Yes. I work on a branch or a staging copy first, test every policy with real accounts, and give you migrations you apply when you are ready.
Do you work with Firebase or plain Postgres too?
Plain Postgres yes, including on Neon or RDS. Firebase is a different model and I would rather point you to someone who lives in it than guess.
What do I actually receive?
SQL migration files in your repository, a diagram of the schema, the policy list with what each one allows, and a short written handover. No slide decks.