Browse categories
English
$
USD
Connect to your AI
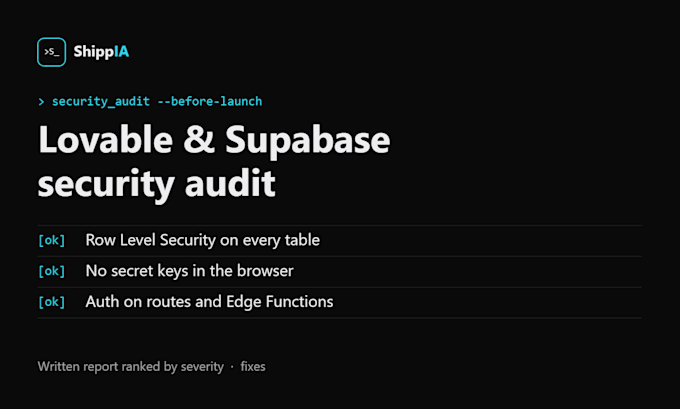
Your app works, but are your users' data actually protected? Apps built with Lovable, Bolt or Supabase often ship with missing Row Level Security, secret keys exposed in the browser, or unprotected routes. I review your project, rank every issue by severity, and tell you in plain words what is at risk and how to fix it. Everything is in writing: a clear report you keep.
What I check: Row Level Security on every table, secret keys exposed in the browser, auth on routes and API endpoints, and Edge Functions.
Audit report: a written report ranked by severity.
Audit + critical fixes: I also fix the blocking issues (RLS policies, auth gaps, key exposure). Key rotation is done by you, on your own accounts.
Launch-ready: plus backups and restore plan, rate limiting, secrets in environment variables, error handling and a final checklist.
I only audit apps you own, with your written authorization. I never ask for your password.
AI Developer, Automations, Web and Mobile Apps, Python, n8n
Languages
Do you need my password?
No. You invite me as a collaborator on your Supabase or Lovable project. You keep full control and can remove my access at any time.
Will you change my live app?
Not without your approval. The Audit report package changes nothing. For fixes, I work on a staging copy first when you have one, and you review each change before it goes live.
Who rotates the exposed keys?
You do, on your own accounts, so no one else ever holds your new keys. I tell you exactly which keys to rotate and how.
Can you audit an app I don't own?
No. I only audit apps you own or are authorized to audit, with your written confirmation before I start.
