Browse categories
English
$
USD
Connect to your AI
Penetration Tester
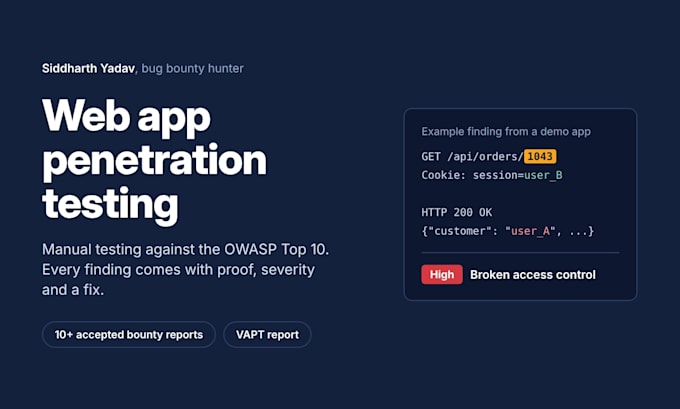
Is your website or web app really secure? I'm Siddharth, a cybersecurity specialist and active bug bounty hunter (HackerOne & Bugcrowd) with 10+ accepted vulnerability reports, including a resolved P2 Account Takeover. I find the flaws real attackers exploit and explain them in plain language.
WHAT I TEST (OWASP Top 10)
- Authentication and session flaws
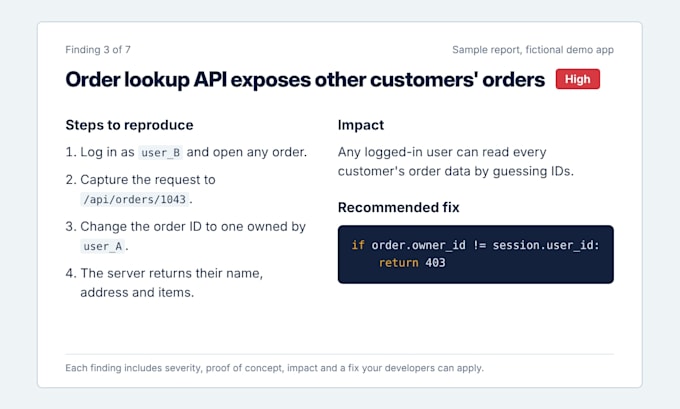
- Broken access control and IDOR
- Injection (SQLi, XSS)
- Business logic and API issues
- Security misconfigurations
WHAT YOU GET
- Detailed report with severity ratings
- Proof of concept and steps to reproduce
- Clear fix recommendations for your developers
TOOLS: Burp Suite, Kali Linux, manual testing
PACKAGES
Basic: scan + short report
Standard: manual pentest of one web app
Premium: full VAPT + API testing + free retest
Testing is done only with your written authorization, and all findings stay confidential. Message me before ordering so we can confirm scope.


Do I need to give you permission to test my site?
Yes. I only test with your written authorization and within the scope we agree on. I’ll send a short confirmation message before starting.
Will testing break or slow down my website?
I avoid destructive tests and heavy load. If you’re worried, I can test a staging copy instead of your live site.
What does the report include?
Each finding comes with a severity rating, proof of concept, steps to reproduce and a recommended fix, written so developers can act on it quickly.
Can you test mobile apps or networks?
This gig covers web applications and websites. Message me first if you need something else and I’ll tell you if I can help.