Browse categories
Explore
Fiverr Pro
English
$
USD
Need help with Splunk SPL, dashboards, alerts, reports or data models?
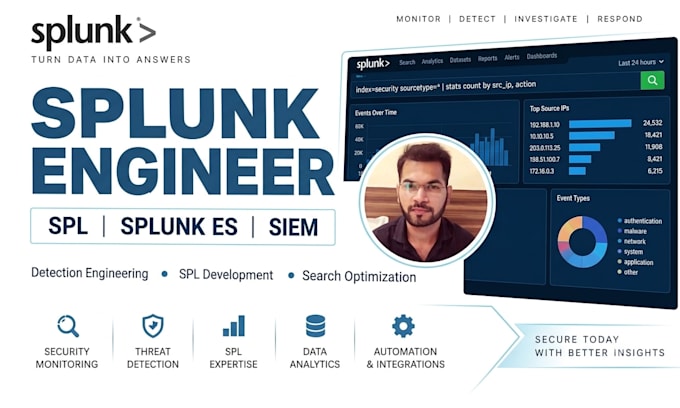
I am a Senior Splunk Engineer with 10+ years of IT experience and 8+ years of hands-on Splunk experience.
I can help you create, troubleshoot and optimize Splunk searches and build practical monitoring and security solutions.
My Splunk services include:
Splunk SPL development and troubleshooting
SPL search optimization and performance improvement
Splunk dashboard creation and customization
Splunk Enterprise Security (ES) detection creation
Security use-case development and tuning
Splunk alert creation and configuration
Scheduled searches and alerts
Splunk report creation and customization
Splunk data model creation and configuration
tstats and data model-based searches
Lookups, joins and subsearches
Field extraction and data validation
Splunk administration troubleshooting
REST API and HEC integrations
Jira/Splunk integrations
Python and Shell automation
I can work with:
Splunk Enterprise
Splunk Cloud
Splunk Enterprise Security
SPL
Data Models
Lookups
Dashboards
Alerts
Reports
Scheduled Searches
What information do you need from me to start?
Please provide your requirement, existing SPL search if available, sample events or relevant field information, expected output, and your Splunk environment/version if known. For troubleshooting, screenshots or error messages are also helpful.
Can you create a Splunk SPL query from scratch?
Yes. I can create SPL searches from scratch based on your monitoring, reporting, investigation, dashboard, or security detection requirements.
Can you optimize an existing Splunk search?
Yes. I can review your existing SPL and optimize its structure, filtering, commands, data-model usage, and overall search efficiency while maintaining the required output.
Can you create Splunk Enterprise Security detections?
Yes. I can develop security detection logic and Splunk ES use cases based on your requirements and available log data. This can include SPL development, detection logic, tuning, testing, and documentation.
Can you work with complex Splunk searches?
Yes. I can work with advanced SPL involving tstats, data models, lookups, subsearches, joins, append, eventstats, streamstats, field extractions, time-based logic, and search optimization.
Can you work with my existing Splunk environment?
Yes, where appropriate. I can review provided searches, configurations, screenshots, sample events, and requirements. Direct access to a production environment is not required for many tasks. Any access requirements for implementation will be discussed before starting.