Browse categories
Explore
Fiverr Pro
English
$
USD
Is your website or API actually secure or just assumed to be?
I'm a Cyber Security student and independent security researcher who finds and reports real vulnerabilities for a living not someone who runs an automated scanner and calls it a "pentest."
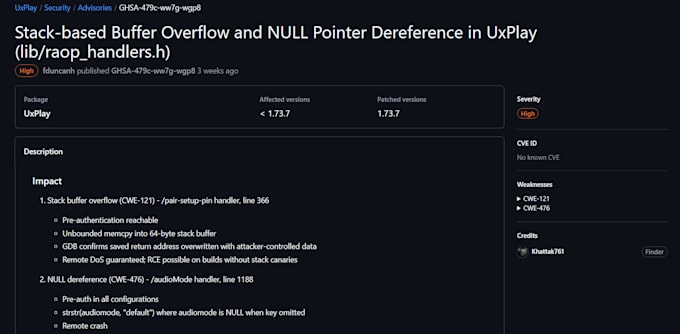
I hold a credited CVE for a real-world vulnerability I discovered and responsibly disclosed, along with multiple published High-severity security advisories for open-source projects through coordinated disclosure. Alongside my research work, I'm part of a CTF team ranked #1 in Pakistan, with several national-level tournament wins under our belt.
What I offer:
Manual web application & API penetration testing (OWASP Top 10 & API Top 10)
SQL Injection, XSS, SSRF, IDOR, Auth Bypass, Race Conditions, Business Logic Flaws
Clear, actionable reports with severity ratings (CVSS) and remediation guidance
Genuine manual testing not a repackaged automated scan
I'm early in my journey as a freelancer here on Fiverr, but the skills behind this gig are proven through real disclosed vulnerabilities, published research, and consistent results in competitive security not just certificates or claims.


Testing application:
Web application
Development technology:
C/C++
•
JavaScript
•
PHP
•
Python
•
SQL
Device:
Linux
What information do you need from me to get started?
Just the URL/API endpoint you want tested, the scope (which pages/endpoints are in-bounds), and written permission to test if it's not your own domain.
Is this a manual test or just an automated scan?
My testing is manual, backed by tools like Burp Suite and OWASP ZAP for coverage not a raw scanner report with no human review.
Do I need technical knowledge to understand the report?
No. Every report includes a clear summary with severity ratings, plus technical details and remediation steps your dev team can act on directly.
Will testing affect my live website or cause downtime?
I test carefully within agreed scope to avoid disruption, but for production systems I recommend testing on staging where possible, or scheduling during low-traffic hours.
Do you sign an NDA?
Yes, I'm happy to sign an NDA before starting if you require one.
What happens if you find critical vulnerabilities?
I'll flag critical/high-severity findings immediately rather than waiting for final delivery, so you can start remediation right away.