Browse categories
English
$
USD
Connect to your AI


Built your app with Lovable, Bolt or Cursor on Supabase? I will audit your Supabase RLS security before someone else finds the holes.
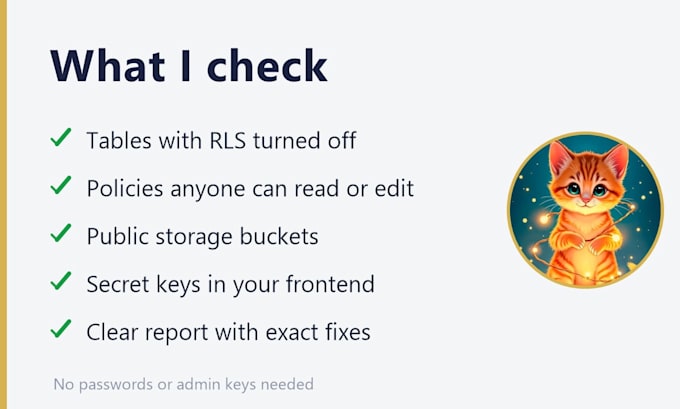
AI builders ship fast, but they often leave data open: Row Level Security switched off, policies that let any visitor read or change data, public storage buckets, secret keys in frontend code.
WHAT I CHECK
WHAT YOU GET
A plain-English report: each problem, how serious it is, and the exact fix. Higher packages include ready-to-run SQL, and Audit and Fix adds a recheck after you run it.
SAFE BY DESIGN
I never need your password or service_role key. You run my read-only SQL script and send me the output. Nothing in your app changes unless you run the fixes yourself.
WHY ME
I build and ship my own web apps with Next.js, React and TypeScript, and I explain things without jargon.
Not sure which package fits? Message me your app link and I will tell you honestly.
Image: Freepik
Full Stack Developer, NextJS Websites, Web Apps, AI Automation
Languages
Do you need my password or admin keys?
No. You run a read-only SQL script in your Supabase dashboard and send me the output. Please never send your service_role key. Any fixes are SQL that you run yourself.
What if my app has more than 5 tables?
RLS Check covers the 5 tables you care about most. Full Audit covers up to 20 tables. For bigger apps, message me for a custom offer.
Will this make my app 100% secure?
No honest audit can promise that. I check the common holes listed above, which are the ones AI-built apps most often have, and tell you exactly what I did and did not check.