Browse categories
Explore
Fiverr Pro
English
$
USD


I complete vendor and customer security questionnaires for your SaaS company using your existing policies, controls, and supporting evidence.
What you receive:
I can work with questionnaires covering information security, privacy, third-party risk, SOC 2, and ISO 27001 requirements.
Please note:
I don't invent or overstate answers your documentation can't support. This service does not include policy writing, control implementation or testing, penetration testing, legal advice, or certification. Questionnaires over the package's limit need an extra or a custom offer.
Please message me first with the questionnaire length, deadline, and available documentation so I can confirm the right package and scope.
GRC Cybersecurity Specialist ISO 27001 27701 42001 Lead Auditor
Languages
What do I need to provide?
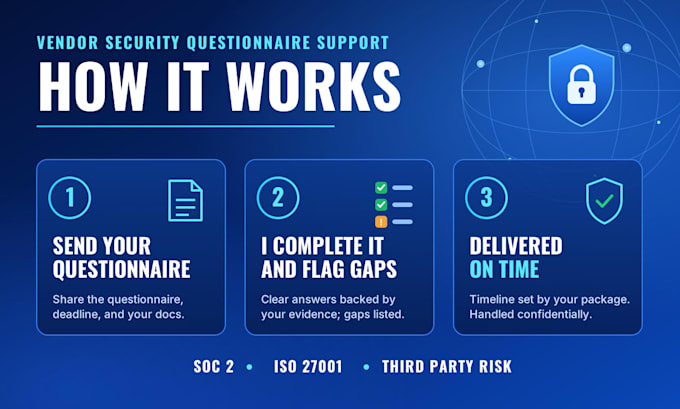
After you place your order, please share the questionnaire, your deadline, your current policies, supporting evidence, and any past responses.
Who is this service for?
SaaS teams needing help completing vendor or customer security questionnaires within a defined scope.
What’s not included?
Policy writing, control implementation or testing, penetration testing, legal advice, certification, or official audit opinions.
What if my documents do not support an answer?
I will flag it in the gap summary and note what evidence or decision is needed. I don’t assume or invent answers.
Can you work with spreadsheets or vendor portals?
Yes, I can work in Excel, Word, or shared docs. For portal-based questionnaires, please export the questions or arrange secure, authorized access after we confirm scope. Never send passwords through Fiverr messages.
Can you sign an NDA?
Yes, I’m willing to review and sign a reasonable NDA before receiving confidential documentation.