Browse categories
Explore
Fiverr Pro
English
$
USD
Security Engineer
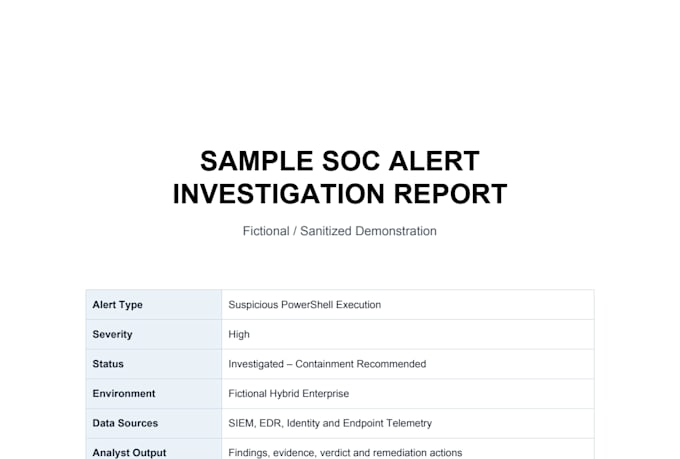
I provide hands-on SOC alert investigation and security log analysis to identify suspicious activity.
With 1.6 years of SOC experience, I investigate security alerts, correlate logs and IOCs, perform threat hunting, and provide practical containment and remediation recommendations.
### Alerts & Investigations
Phishing and malicious email alerts
Malware and endpoint security alerts
Credential compromise and suspicious authentication
Account takeover and MFA-related activity
Brute-force and credential-stuffing activity
IOC investigation and threat hunting
Suspicious processes and command execution
Web exploitation and WAF alerts
Firewall and network security alerts
Privilege misuse and suspicious account activity
### Tools
SIEM: Datadog, Splunk, Microsoft Sentinel, Kibana
EDR: CrowdStrike, Microsoft Defender
Firewall: Palo Alto, FortiGate
WAF/Proxy: Imperva, Bluecoat
Email Security: Microsoft Defender for Office 365, Symantec
Cloud/Identity: Azure, Entra ID, OCI
Network: HAProxy
### What You Receive
Alert triage and investigation
Log and IOC correlation
Threat-hunting findings
Investigation summary
Recommended containment and remediation actions
Relevant indicators and evidenc