Browse categories
Explore
Fiverr Pro
English
$
USD
Fullstack Lead Developer with 8 years' experience
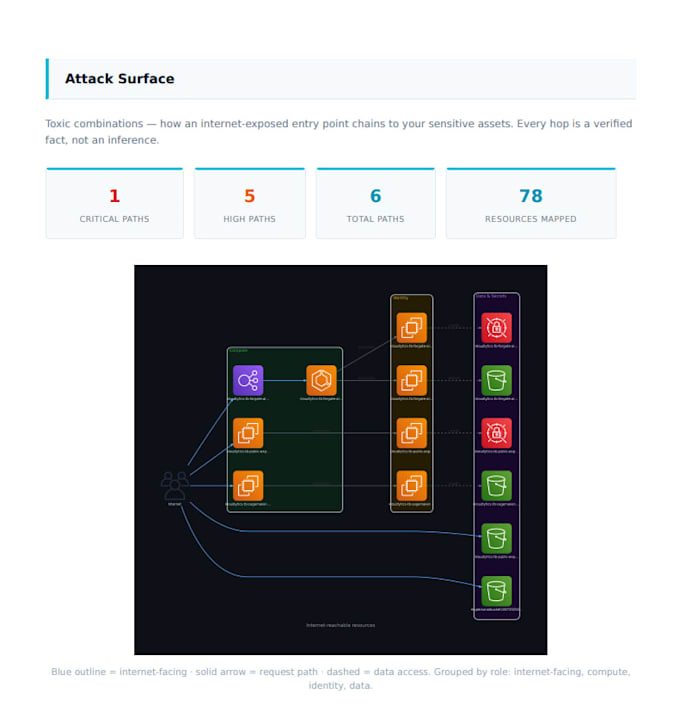
Hi, I can provide you a quick report on your AWS infrastructure. 200+ security checks across 36+ AWS services including Bedrock and SageMaker with attack-surface mapping, and a posture score.
I won't need any write access to your AWS account. You just need to create a read only role for which I will provide a cloud formation template.
Cloud formation template will be transparent and you will be able to see what exact permissions I require.
Get in touch and let's secure your cloud!!!!


Cloud provider:
Amazon Web Services
Expertise:
Configuration
•
Performance
Cloud computing resource:
ELB
•
Route53
•
VPC
•
Security Groups
•
DNS
What AWS permissions are required?
only requires read-only IAM permissions. We use AWS managed policies (SecurityAudit, ReadOnlyAccess) scoped to the services we analyse. I never request write permissions of any kind.
How does cross-account access work?
You create an IAM role in your AWS account with a trust policy that allows my AWS account to assume it. The role requires a unique external ID we generate — this prevents confused deputy attacks where another AWS customer could trick AWS into granting them access.
Is anything get installed in my environment?
No. it is fully agentless. We connect to your account via the AWS API using the STS AssumeRole API. Nothing is installed, deployed, or run inside your AWS account.
How long are credentials valid?
We uses STS AssumeRole to generate short-lived temporary credentials for each scan. These credentials expire automatically and are never stored long-term.