Browse categories
Explore
Fiverr Pro
English
$
USD
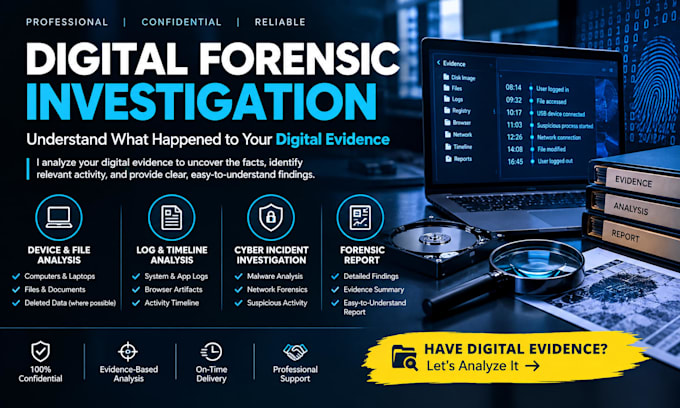
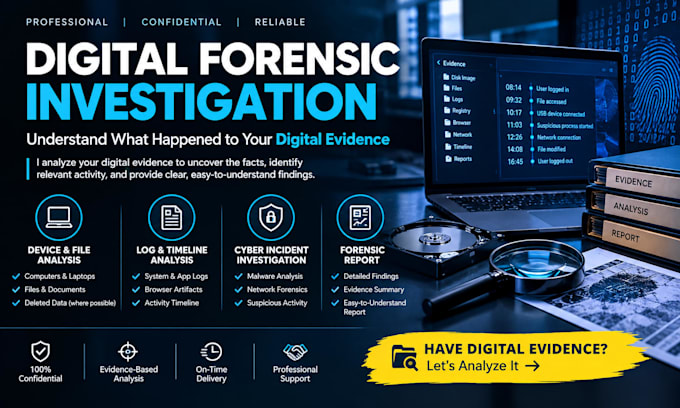
Need help understanding what happened to your device, files, logs, or digital evidence?
I will perform a professional digital forensic analysis of your authorized digital evidence and provide clear findings in a structured forensic report.
Whether you're dealing with suspicious activity, deleted files, unusual system behavior, security incidents, or digital evidence that needs examination, I can help analyze the available data and turn technical findings into an understandable report.
What I can analyze:
Send me a message before ordering if you're unsure whether your evidence or case is suitable for analysis.
Important: Services are limited to digital evidence and systems you own or are explicitly authorized to examine. I do not assist with unauthorized access, credential theft, spying, or other unlawful activity.
Operating system:
Windows
•
Linux
•
Unix
•
IOS
•
Android
What do you need from me to start?
I need the digital evidence or forensic data you are authorized to provide, along with a description of the investigation objective and any relevant background information.
Can you analyze a forensic image?
Yes, I can work with supported forensic images and extracted evidence, depending on the format, condition and scope of the case.
Can you investigate suspicious activity?
Yes. I can examine supplied digital evidence for relevant artifacts, activity, timelines, logs and indicators associated with the issue.
Will I receive a report?
Yes. The selected package determines the depth and scope of the report.
Can you recover deleted files?
Where technically possible, deleted or recoverable artifacts can be examined. Recovery is not guaranteed because results depend on the condition of the underlying data.