Browse categories
English
$
USD
Connect to your AI
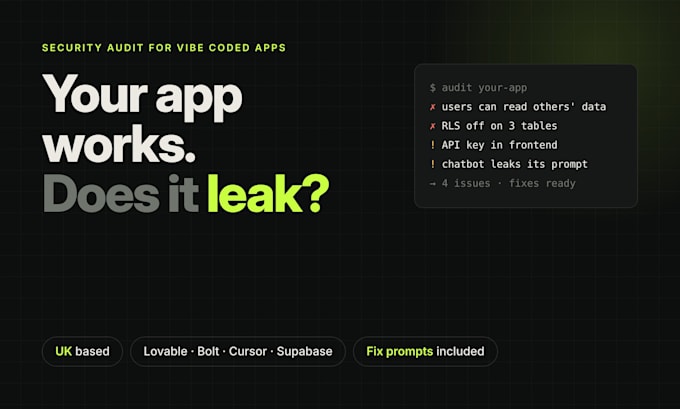
Built your app with Lovable, Bolt, Cursor, Replit or v0? It probably works. It probably also leaks.
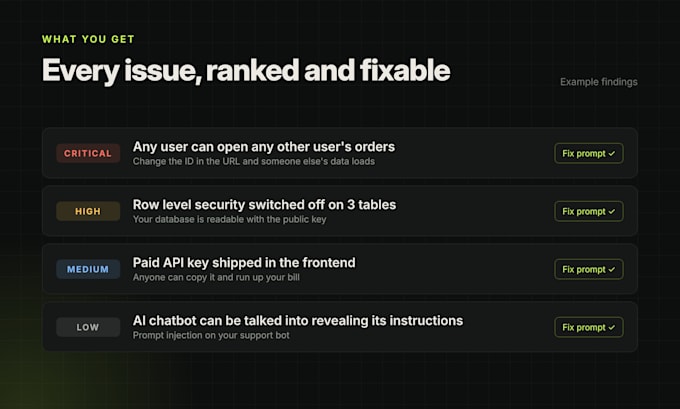
AI coding tools ship fast and skip security. I see the same problems again and again:
I find these, show you exactly how each one can be exploited, and explain the fix in plain English. On the top package I fix them for you.
Why me
What you get
I only test apps you own or have written permission to test.
Message me with your stack before ordering and I'll tell you what Id check.
UK developer, I find the security holes in vibe coded apps
Languages
Can I message you in my own language?
Yes. Write to me in any language and I’ll reply in yours using translation tools. The report comes in English by default, and I can translate the summary if you need it.
What do you need from me?
Your live app URL, read access to your GitHub repo, and two test accounts so I can check whether one user can see another’s data. I can test from the URL alone, but the repo makes the audit much more thorough.
Will testing break my live app?
No. I don’t run load tests, delete data or change anything on your live app. On the Audit + Fix package, all fixes go through a pull request that you review before anything is merged.
My app wasn’t built with Lovable. Can you still help?
Yes. If it’s built on Next.js, React, Node, Supabase, Firebase or Postgres, I can audit it, however it was made.
What if you don’t find anything?
You still get a report showing everything I checked and that it passed. That’s useful proof if you’re launching, raising money or onboarding clients.
Is my code kept private?
Yes. I only use it for your audit, and I remove my access once the order is delivered. I’m happy to sign an NDA if you need one.
Can you fix the issues too?
Yes. Pick Audit + Fix, or add the Fix one issue extra to any package.