Browse categories
Explore
Fiverr Pro
English
$
USD
Cybersecurity Resume and Career Support SOC GRC TPRM
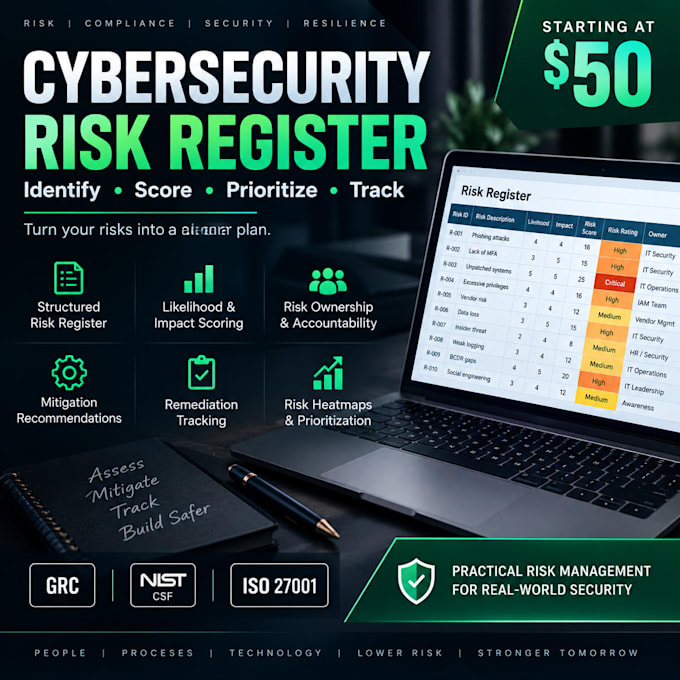
I help businesses and teams organize cybersecurity risks into a clear, structured risk register.
A risk register helps you understand what could go wrong, how serious each risk is, who owns it, and what should be done about it.
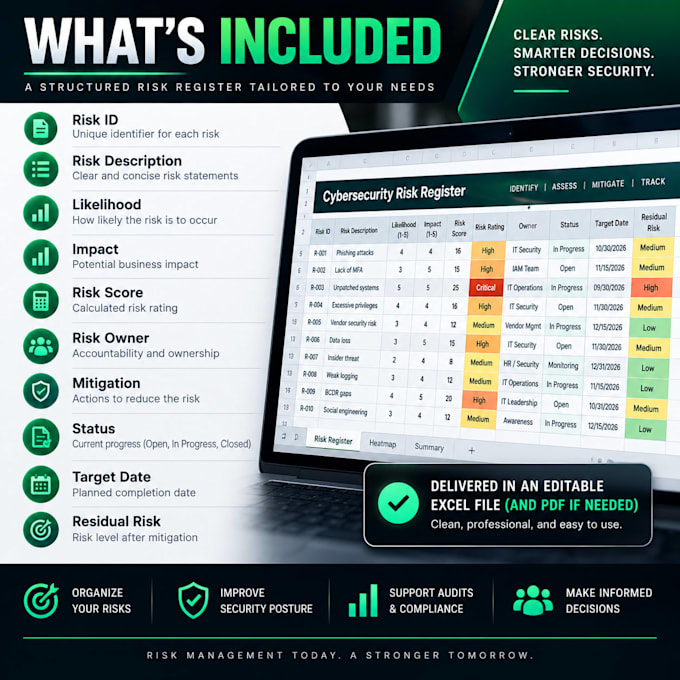
I can create or improve a cybersecurity risk register that includes:
This service can support GRC, cybersecurity assessments, internal audits, vendor risk reviews, ISO 27001 preparation, NIST-based risk management, and general security planning.
I focus on practical documentation that is easy for both technical and non-technical stakeholders to understand.
This service supports risk documentation and analysis and does not replace legal, regulatory, or formal audit advice.


Business type:
Startups
•
Corporates
Industry:
Business services & consulting
•
Cyber security
Can you build a risk register from scratch?
Yes. If you provide your environment, systems, risks, or assessment findings, I can organize them into a structured risk register.
Can you improve an existing risk register?
Yes. I can clean up risk statements, scoring, ownership, mitigation actions, status tracking, and overall structure.
What frameworks can this support?
The register can support general GRC work and frameworks such as NIST CSF and ISO 27001.
Do you guarantee compliance or audit success?
No. This is a documentation and risk-management support service. It does not guarantee certification, compliance, or audit results.