Browse categories
Explore
Fiverr Pro
English
$
USD
The Cyber Friend, where you can Trust Us, with your Security
Sam was selected by the Fiverr Pro team for their expertise.
Vetted for
Cybersecurity
Vetted Pro
Most tabletops are checkbox theater. A facilitator reads from a script, leadership nods along, and the report goes in a folder nobody opens again.
This is not that.
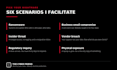
I build the scenario around your actual exposure. Ransomware if downtime would end you. Insider threat if privileged access worries you. Vendor breach if your supply chain is the weak link. Regulatory inquiry if an audit is coming.
Every exercise includes:
This satisfies HIPAA 164.308(a)(7), the CMMC Level 2 incident response domain, and NIST CSF RS.RP. When your insurer asks whether you have tested your plan, this is the document that answers.
Nothing goes down, and nobody touches production. Your team makes decisions in a room and finds out where the plan breaks while it is still cheap to find out.
Message me with your industry and what is driving this, and I will tell you which scenario fits.



Expertise:
Awareness
•
Gap Analysis
•
Risk Assesment
Technology:
Cloud - IaaS
•
Mail Services
•
Physical
•
Saas
•
Databases
Who is this for?
Any organization that needs to test its incident response plan, satisfy a compliance requirement, or prepare leadership for a real incident.
What scenarios can we run?
Ransomware, insider threat, third-party or vendor breach, regulatory inquiry, business email compromise, data exfiltration, and physical security incidents. We pick the scenario together based on your industry, your actual exposure, and what your auditor or insurer wants documented.
How long does the actual exercise take?
The facilitated session itself is 2 hours. Plan for an additional 30 to 45 minutes at the front end for a kickoff call to scope the scenario, and another 30 minutes after the exercise for an immediate hot-wash debrief.
Does this satisfy our compliance requirement?
It maps to HIPAA 164.308(a)(7), the CMMC Level 2 incident response domain, and NIST CSF RS.RP. You get written documentation showing the exercise happened, what surfaced, and what you are doing about it.
Do you need access to our systems?
No. Nothing goes down, and nobody touches production. This is a facilitated discussion. Your team makes decisions in a room, and we document where the plan breaks.
Who needs to be in the room?
Whoever would actually make the calls during an incident. Owner or executive, IT lead or provider, and anyone owning legal, HR, or communications. Six to ten people work best. More than twelve and the quieter voices stop talking.


