Browse categories
English
$
USD
Connect to your AI
CMMC, HIPAA and NIST compliance advisor, CISM, CMMC RPA
Sam was selected by the Fiverr Pro team for their expertise.
Vetted for
Cybersecurity
Vetted Pro
Your PTIN expires December 31. Renewing means certifying on Form W-12 that your firm has a written information security plan. Falsely certifying is perjury, and the IRS can suspend the PTIN you need to file with.
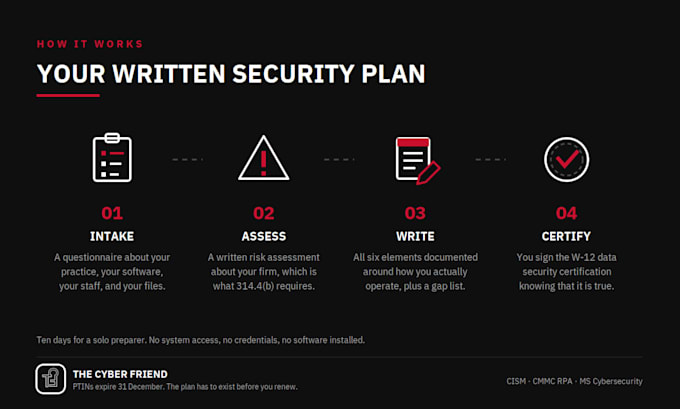
Most preparers download IRS Publication 5708, open it once, and close it. It is a sample. The risk assessment below must describe your practice, systems, and staff because that is what 16 CFR 314.4(b) requires.
I write yours.
What you receive:
The document is editable and yours, with guidance on the annual review the rule requires.
Message me with the number of preparers in your firm, and I will tell you which tier fits.


Expertise:
Awareness
•
Data Protection
•
Risk Assesment
Technology:
Cloud - IaaS
•
Mail Services
•
Saas
Regulation:
Other
Am I actually required to have a WISP?
Yes. The FTC Safeguards Rule requires every financial institution to maintain a written information security program, and GLBA classifies tax preparers as financial institutions. IRS Publication 4557 provides guidance on what it must contain. Firm size is not an exemption.
The IRS gives away a free template. Why pay for this?
5708 is a sample. The rule requires a written risk assessment that describes your practice, systems, and staff, and the plan must reflect it. A sample completed generically does not do that, and it is the part an FTC inquiry looks at first.
What does this have to do with my PTIN?
Form W-12 asks you to certify that a data security plan exists. Certifying falsely is perjury and can cost you your PTIN, which ends your ability to file for compensation. PTINs expire on December 31, so the plan needs to be in place before you renew.
What are the six required elements?
A named Qualified Individual, a written risk assessment, a safeguards program, service provider oversight, an incident response plan, and regular review and updating. All six have to be documented, not just intended.
Who is the Qualified Individual?
The rule allows the Qualified Individual to be your own staff or an outside service provider. For most small firms, it is the owner or managing partner, and I document what that role is accountable for. If you want me in the role, that is a retainer, and we talk separately.
Do you check that our security is actually in place?
I document what you actually run and flag what is missing. This is questionnaire-driven, so I never access your systems or request credentials. Anything required that you do not yet have comes back as a gap, with what to do about it.
How long does it take?
10 days for a solo preparer, 14 for a firm, 21 for multiple entities. The clock starts when your intake answers come back. During October through December, I hold those times, so order early rather than the week of renewal.
Does this include staff training?
You get the documentation and materials showing that training is required and what it must cover. I do not run the session inside this package. If you want training delivered, I have a separate gig for it.
We have more than 5,000 client records. Does that change anything?
Firms with over 5,000 customer records are subject to additional Safeguards Rule requirements, including annual penetration testing. I do not perform penetration testing. If that threshold applies to you, tell me before ordering, and I will tell you what else you need.
Do we need to redo this every year?
The rule requires review at least annually and after any material change, such as new staff, new software, a new office, or an incident. Order the review again next year, and I will update it. It is faster and cheaper than the first build.