Browse categories
English
$
USD
Connect to your AI
Full Stack Developer API Integrations and Security
Hi, I'm Mohamed :) a developer who also does penetration testing, so I look at your code the way an attacker would.
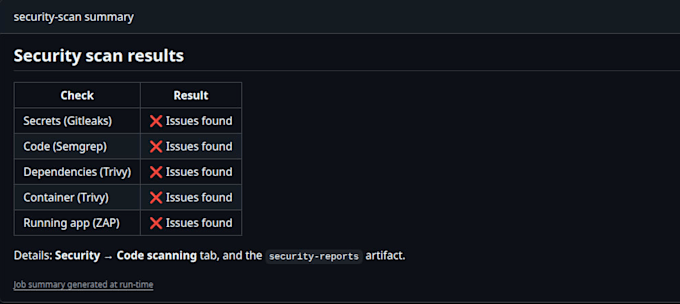
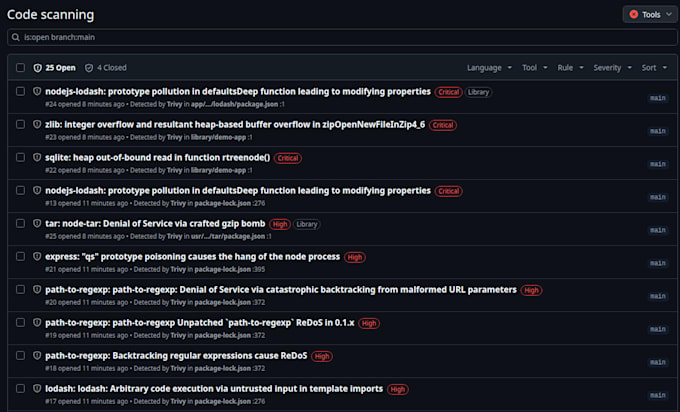
I set up automatic security checks in your CI/CD pipeline. Leaked passwords, risky packages, and common vulnerabilities get flagged before you ship, not after.
What you get
Scans for leaked secrets, vulnerable packages, and insecure code on every commit
Docker image scanning
Slack or email alerts with plain-English fixes
Staging app testing and manual review (Premium)
Help choosing the right tools for your stack
I work with GitHub Actions and GitLab CI, using tools like Gitleaks, Semgrep, Trivy, and OWASP ZAP. I tune each setup so you're not buried in false alarms.
I only test systems you own or have permission to tessecurity, but this catches the common problems early.
Not sure which package fits? Message me with your sta right one.

Do you need access to my production environment?
No. Read access to your repo is enough. I only need a staging URL for the Premium dynamic scan.
Which CI platforms do you work with?
GitHub Actions and GitLab CI. If you use something else, message me first and I'll tell you if I can help.
Will this slow down my builds?
Barely. I set scans to run in parallel or only on pull requests, so they add minutes, not hours.
Do I need to give permission before you test my app?
Yes, for staging scans. I need written confirmation that you own the app or are authorized to test it.
I'm not sure which package I need. What should I do?
Send me a message with your tech stack and what you're worried about. I'll recommend the right package before you order.