Browse categories
English
$
USD
Connect to your AI



Need SOC 2 or ISO 27001 to close an enterprise deal, but not sure how far you are from audit-ready?
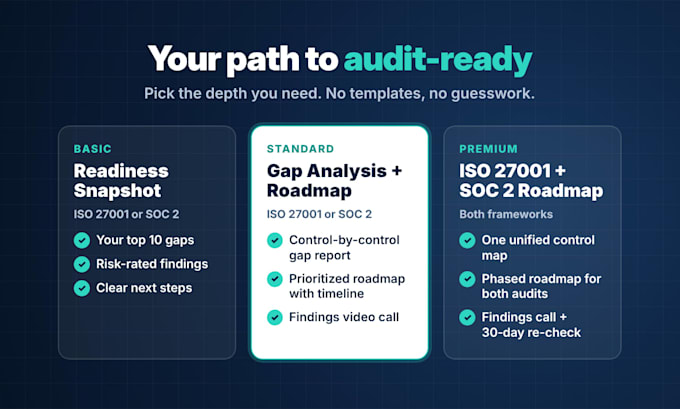
I'll assess your current security practices against SOC 2 (Trust Services Criteria) or ISO 27001:2022 (clauses and Annex A), show you exactly what's missing, and give you a prioritized roadmap to certification.
What you get:
Why work with me:
I also implement controls in Microsoft 365, Entra ID, and Intune, so your roadmap is practical, not theoretical.
Not sure which package fits? Message me first, and I'll confirm the right scope.
ISO 27001 Lead Auditor, SOC 2, ISO 42001 and Microsoft 365 Security
Languages
Do I need ISO 27001, SOC 2 or both?
US customers usually ask for SOC 2; EU and global customers often ask for ISO 27001. Tell me who you sell to and I'll recommend one. If you need both, Premium maps them together so you build each control once.
Will this get me certified?
It shows exactly what to fix before your audit. The audit itself is done by an independent party: an accredited certification body for ISO 27001, or a licensed CPA firm for a SOC 2 report.
SOC 2 Type I or Type II: which do you cover?
Both. Type I checks your controls are designed correctly at one point in time; Type II checks they ran for 3-12 months. I'll flag which gaps block Type I and what you need to start collecting for Type II.
What do you need from me?
Answers to the order questions, any policies or past audit reports you have, and a 30-60 minute call or questionnaire with whoever runs your IT and security. No admin access to your systems is needed.
Do you work with Vanta, Drata or Secureframe?
Yes. I'm a Verified Vanta Admin. If you already use a compliance platform, I'll use your control and test status as input, so the roadmap fits the tool you have.
Do you also write the missing policies?
Not in this gig. Your report lists every missing or weak policy. If you want them written, I offer that as a separate policy service. Message me and I'll send a custom offer.
What does systems/assets in scope mean?
The products or platforms that will be in your audit scope, for example your main SaaS app and its cloud environment. Most startups need 1. Message me if you have more.