Browse categories
Explore
Fiverr Pro
English
$
USD
OSCP, CEH Master, CPENT, Penetration Tester and Security Consultant
Level 1
Has met certain performance criteria and shows strong potential in the marketplace.
Automated scanners produce noise. This is a manual, line-by-line security review of your source code by a penetration tester, combined with SAST tooling, so you get findings your developers can actually act on.
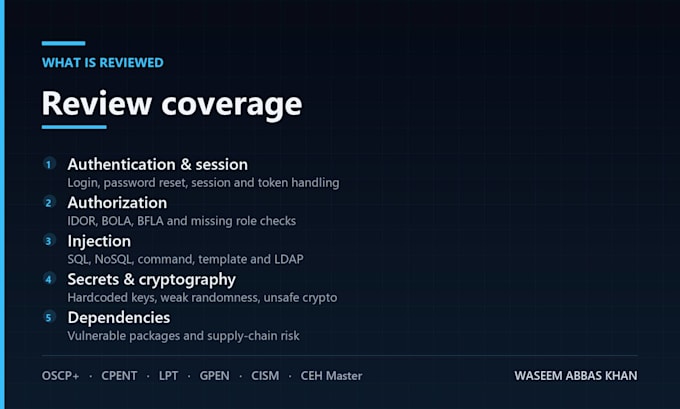
I review for:
- Authentication and session management flaws
- Authorization and access-control gaps (IDOR, BOLA, BFLA)
- Injection: SQL, NoSQL, command, template and LDAP
- Unsafe deserialization and file upload handling
- Secrets and credentials committed to the repository
- Cryptographic misuse and weak randomness
- Dependency and supply-chain risk
- Logging, error handling and data exposure
Each finding includes the file and line reference, a clear explanation, proof of concept where safe, severity (CVSS 3.1) and a code-level remediation example. I can follow your stack: Python, Node.js, PHP, Java, .NET, Go, Ruby or TypeScript.
Basic: up to 5,000 lines, one language.
Standard: up to 20,000 lines, two languages, dependency review.
Premium: up to 50,000 lines, full manual review, remediation workshop and retest.
Send me the repository link or an archive, plus a short note on what worries you most.
Device:
Desktop
•
Laptop
•
Server
•
Mobile
•
Tablet
Operating system:
Windows
•
Linux
•
Unix
•
Android
My code is private. How do you access it?
Private repository invite, zip archive or a shared branch. Access is removed at the end of the engagement.
Do you sign an NDA?
Yes. Send yours, or I can provide a mutual NDA.
Is this the same as a pentest?
No. This is white-box source review; it finds issues earlier and points to the exact line of code.